

Most of our readers who participated in EthiHak as part of Infocom Security 2016 are anxiously awaiting the solution to the competition! The moment has come and we are happy to announce one of the proposed solutions!
The EthiHak Scenario:
- Finding a SQL Injection vulnerability on a specific site.
- Exploiting this weakness and lowering the base shape.
- Within the database schema there is the 'contact_persons' table through which the attacker will receive information about his next steps.
- From the above table it will find (among others) emails with the aim of sending malware to gain access to the box/es where the recipients of the emails are located. The victims' PCs are running Windows 7 (full patched) with Microsoft's Windows Essentials enabled as well as the default Firewall.
- To entice them to open the email and “take the bait”, he must use Social Engineering techniques. For this reason, our “victims” have a rich Social Network… (fb, linked in).
- The attacker must gain access to the user's Local Box to write some files there that will prove his intrusion.
- Immediately after that, it will need to find and exploit the network where the compromised computer is located.
- He will therefore have to discover that the victims' computers are set up in an Active Directory as well as find the corresponding Domain Controller Server.
- The Domain Controller Server is a Windows 2008 R2 (full patched) with Microsoft's Windows Essentials enabled and the default Firewall. However, it has a relatively weak password that can be found in a good dictionary.
- The completion of the scenario is achieved by capturing the Domain Controller and uploading some files there that prove the intrusion.
- Finally, the perfect approach would be for the attacker to find and provide in the final report some files that exist on the various PCs or on the Server that contain sensitive data and that if someone were to publish them, would greatly negatively affect the reputation of the specific company.
Proof of Concept (pOc)
First of all, let us emphasize that the problem is not deterministic. Any solution, finding and exploiting any weakness is acceptable, as long as it brings about the desired result. During the evaluation, the most intelligent and original approach was chosen, as well as the one that "advanced" the most.
We will now present an approach to solving the problem, but in no way should it be considered the only correct one or the one that will be rated with the Best Points. Let it simply be considered as one of the many Proof Of Concepts that could exist for this particular Challenge.
Step 1: SQL Injection
The vulnerability is located on the page: https://www.havesec.com/news.php?id=1
It can be exploited very easily, both manually and with automatic tools.
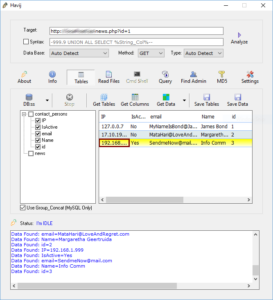
We list the manual steps that lead to displaying the data in the contact_persons table .
- Get Tables
https://www.havesec.com/news.php?id=1 union SELECT table_name FROM information_schema.tables - Get Columns per table
https://www.havesec.com/news.php?id=1 union SELECT concat(table_name, ' | ', column_name) FROM information_schema.columns
3.Get full data for table contact_persons
https://www.havesec.com/news.php?id=1 union select concat(isActive, ' | ', id, ' | ', ip, ' | ' , name, ' | ', email) from contact_persons
Also, as an automatic way, one could use e.g. Havij, see next image:
Step 2: Information Gathering
The attacker will use the Social Network for Information Gathering. He will get material in order to find out what the victims' weaknesses are. For example, our wonderful secretary, Sevi, has a weakness for… sexy lingerie among other things, while our very CEO likes extreme Sports.
Step 3: Social Engineering & Phishing
With the information gathered from the previous step, the attacker can create an email and send it to one of the victims of his choice. The message may have an attachment (or a link) that the victim is invited to click on, but it may be delivered in such a way as to exploit the victim's weaknesses... e.g.
The new line of X silk luxury underwear is now at an introductory price with 80% off.
Please click here to download the offer coupon.
...or at least something similar.
Step 4: Payload Execution
In this step, the attacker must have a good enough Payload that the victim will download to their PC, in order to accomplish the following:
- Run without being detected by Antivirus.
- Allow the attacker remote access (classic RAT case).
- The RAT must only "listen" to one of the ports 80 or 443, given that the victim's PC is located on another network, behind a firewall, a corporate router, etc.
What was needed here is to run a relatively simple RAT (home-made or via metsasploit) that allows remote execution, runs on one of the above ports, and can transfer files from the attacker's PC to the victim's PC. Of course, this latter is optional since someone could put the "necessaries" in a good (aka undetectable) container and download them to the victim's PC in the attached file of the phishing email. We transferred THC_Hydra, which we will use in our next step. Of course, in such cases, it is good for someone to transfer with the very useful wget (https://goo.gl/7ikGUo) for Windows so that we can... download whatever we "like" at will. With exactly the same logic, we also download the very useful PSExec (https://goo.gl/iscr9M). We will use this tool to get a shell on the... server (next step).
Step 5: Domain Server attack
The attacker's final step was to find the Domain Server and Pown it.
There are several ways to find the Domain Server from an already Logged In client. For example, with the command echo %LOGONSERVER% we can get its name.
Immediately afterwards, we could use a Dictionary attach tool to try to crack the Administrator password.
The tool we used is the well-known THC_Hydra, which we can immediately download and execute through our RAT:
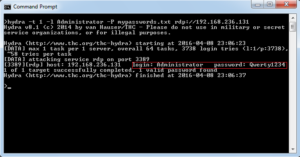
Immediately afterwards we execute PsExec with the… similar results!!
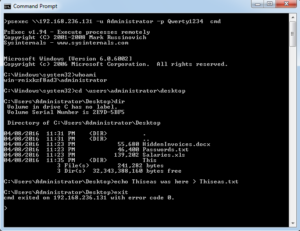
TIP: The first time you call parameter /accepteula so that the banner accepting the execution of the command does not appear on the unsuspecting victim's screen , which would probably... betray you!
Stay tuned for all the hacking competitions organized by Secnews.gr as well as information about the next EthiHak!
Happy Ethical Hacking!! 😉
