


The Cybercrime Prosecution Directorate informs citizens about the dissemination of a malicious software (Backdoor Trojan), which spreads with the appearance of a post with a pornographic video on the social networking website "Facebook"..
Specifically, the post in question appears to have been shared by a friend of the user on "Facebook" and up to twenty (20) of his friends have been tagged in it.
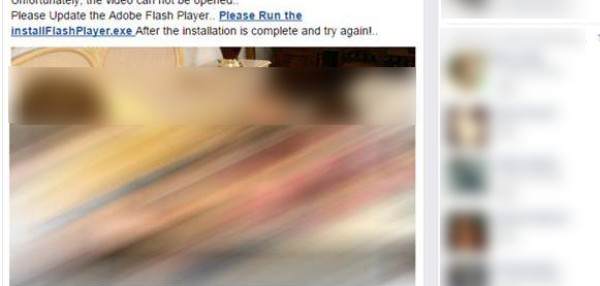
If the user clicks on what appears to be pornographic video, they are taken to a fraudulent website where the first few seconds of the video play and then its playback stops and a message appears, informing the user that they are required to "download" an upgrade of the Adobe Flash Player software (InstallFlashPlayer.exe), as shown in the following image:
If the user consents and "downloads" the file, then he is infected by malicious software (Backdoor Trojan), which has the ability to "monitor" the keyboard and "mouse" of the infected computer, as a result of which codes and communications of all kinds can be intercepted (e.g. e-banking codes, credit card numbers, email passwords, etc.).
In addition , the malicious software has the ability, after its installation and infection of the computer, to automatically upload the pornographic video in question to the user's "Facebook" account, simultaneously tagging up to twenty (20) of his friends, with the aim of further self-propagation. In this way, the malicious software spreads, through the "Facebook" platform, infecting a large number of computers.
Internet users are urged to be particularly careful and take the following minimum protection measures:
– Do not click on posts with strange content or posts that do not appear to lead to a known website.
- From the security settings of "Facebook", activate the option in which no one will be able to tag them without their approval.
- Use security applications, such as Antivirus software, which should always be updated.
- Check and always keep the version of their computer's operating system updated.
Source: newsit.gr
