

The North Korean hacking group Lazarus is behind a new attack that involves distributing fake cryptocurrency apps under the invented brand “BloxHolder.” In doing so, they install the AppleJeus malware, which gives them initial access to networks and ultimately allows them to steal crypto assets.
The AppleJeus malware has been around since at least 2018 and is used by Lazarus for cryptocurrency theft operations, as stated in a joint FBI and CISA report from February 2021.
A new report from Volexity has identified new, fake ransomware and AppleJeus activity, with signs of evolution in the infection chain and malware capabilities.
See also: Microsoft account: 7 essential security tips

New BloxHolder campaign
The new campaign attributed to the Lazarus group began in June 2022 and was active at least until October 2022.
In this attack, hackers exploited the domain “bloxholder[.]com”, which is a clone of the automated cryptocurrency trading platform HaasOnline.
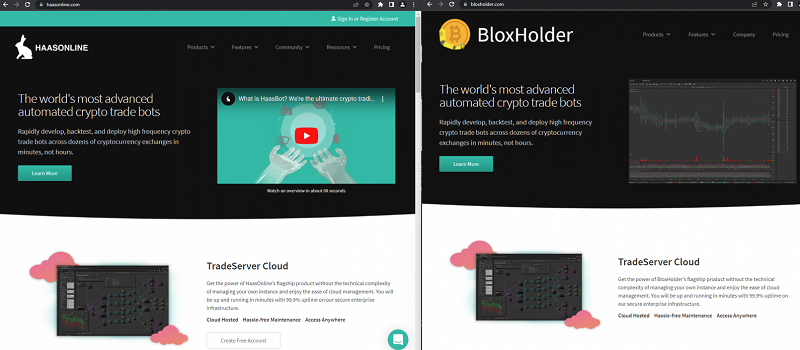
This website distributed a 12.7 MB Windows MSI installer that pretended to be the BloxHolder application. However, in reality, it was the AppleJeus malware bundled with the QTBitcoinTrader application.
In October 2022, the hacking group evolved its campaign to use Microsoft Office instead of the MSI installer to distribute the malware.
The 214 KB document was named “OKX Binance & Huobi VIP fee comparision.xls” and contained a macro that creates three files on a target’s computer.
Volexity was unable to find the final payload from this later infection campaign, but they noticed similarities in the DLL sideloading mechanism found in MSI installer attacks used in the past, so they are confident that this is the same campaign.
See also: US: Defense contractors fail to meet basic cybersecurity requirements
When installed via the MSI infection chain, AppleJeus will create a scheduled task and drop additional files to the “%APPDATA%\Roaming\Bloxholder\” folder.
Finally, the malware gathers information such as the MAC address, computer name, and operating system to send to the C2 server via a POST request. The purpose of the data is likely to determine whether it is running in a virtual machine or sandbox.
A new method that some malicious actors are using to load malware is called chained DLL sideloading, which loads the malware inside a trusted process and therefore evades detection by AVs.
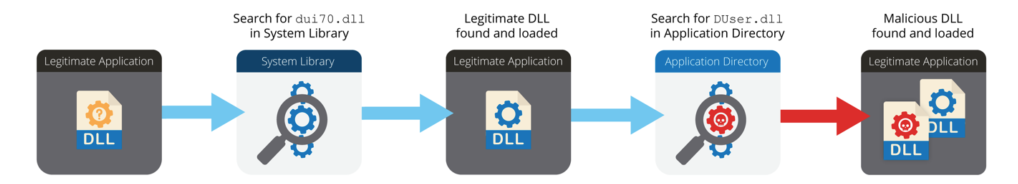
Volexity says the reason the Lazarus team chose chained DLL sideloading is unclear, but it may be that it hinders malware analysis.
Another new feature in the recent AppleJeus samples is that all of its stings and API calls are now obfuscated using a custom algorithm, making them more stealthy against security products.
Although Lazarus' focus on cryptocurrency assets is well-documented, North Korean hackers remain steadfast in their goal of stealing digital money, constantly updating themes and improving tools to remain as stealthy as possible.
What is the Lazarus Group?
The Lazarus Group, also known as ZINC, is a North Korean hacking group that has been operating for over a decade.
The group gained notoriety after successfully carrying out a cyberattack on Sony Films, and the 2017 global WannaCry , which encrypted businesses around the world.
In January 2021, Google discovered that the Lazarus group was creating fake online personas to trick security researchers into social engineering campaigns that installed backdoors on their devices. A second attack using this tactic was discovered in March 2021.
In September 2019, the US government put Lazarus on notice, imposing sanctions on it, and is now offering a $5 million reward for any information that could help stop activities .
See also: Google Play: Malicious apps with 2 million downloads
In the most recent attacks, they have turned to the spread of trojanized cryptocurrency wallets and trading applications that steal people's private keys and drain their crypto assets .
In April, the US government linked the Lazarus Group to a cyberattack on Axie Infinity that allowed them to steal over $617 million worth of Ethereum and USDC tokens
It was later revealed that the Axie Infinity hack was made possible by a phishing attack that contained a malicious PDF file pretending to be a job offer sent to one of the company's engineers.
Information source: bleepingcomputer.com
