

NVIDIA has released a security update for a wide range of graphics card models, addressing four high-severity and six medium-severity vulnerabilities in its GPU drivers.
See also: NVIDIA Unveils Grace CPU Superchip

The security update fixes vulnerabilities that could lead to denial of service, information disclosure, elevation of privilege, code execution, and more.
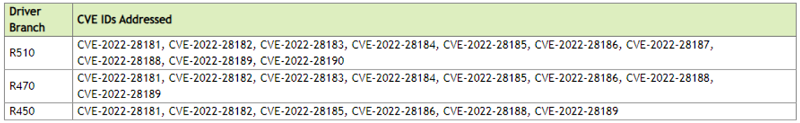
Updates have been made available for Tesla, RTX/Quadro, NVS, Studio, and GeForce software products, covering driver branches R450, R470, R470, and R510.
Interestingly, in addition to the current and recent product lines that are actively supported, NVIDIA's latest release also covers the GTX 600 and GTX 700 Kepler series cards, whose support ended in October 2021.
See also: Instant NeRF from NVIDIA: Converts 2D photos into 3D scenes
The GPU manufacturer previously promised to continue providing critical security updates for these products until September 2024, and this driver update honors that promise.
The four high-severity flaws fixed this month are:
- CVE-2022-28181 (CVSS v3 score: 8.5) – Out-of-bounds write at the kernel mode level caused by a specially crafted shader sent over the network, which may lead to code execution, denial of service, privilege escalation, information disclosure, and data corruption.
- CVE-2022-28182 (CVSS v3 score: 8.5) – Flaw in the DirectX11 user mode driver that allows an unauthorized attacker to send a specially crafted shared asset over the network and cause denial of service, privilege escalation, information disclosure, and data corruption.
- CVE-2022-28183 (CVSS v3 score: 7.7) – Kernel mode vulnerability, where an unprivileged regular user can cause an out-of-bounds read, which can lead to denial of service and information disclosure.
- CVE-2022-28184 (CVSS v3 score: 7.1) – Vulnerability in the kernel mode layer handler (nvlddmkm.sys) for DxgkDdiEscape, where a normal unprivileged user can access registries with administrator privileges, which can lead to denial of service, information disclosure, and data corruption.
These vulnerabilities require low privileges and no user interaction, so they could be incorporated into malware, allowing attackers to execute commands with higher privileges.

The first two are exploitable over the network, while the other two are exploited with local access, which could be useful for malware infecting a system with low privileges.
See also: Nvidia: Linux GPU drivers will be open source
Cisco Talos, which discovered CVE-2022-28181 and CVE-2022-28182, published a post today detailing how the flaws caused memory corruption by providing an incorrect compute shader.
As threat actors can use a malicious shader in the browser from WebAssembly and WebGL, Talos warns that threat actors may be able to activate remotely.
For more details on all the fixes and every software and hardware product covered this month, please refer to NVIDIA's security bulletin.
All users are advised to apply the security updates that have been released as soon as possible. Users can download the latest driver for their GPU model from NVIDIA's central download section, where they can select the specific product and operating system they are using.
Information source: bleepingcomputer.com
