

The cyberattack on multiple targets of the General Secretariat of Commerce aimed to post a message and has not been detected until now.

Mass alteration of websites with parallel posting of messages to the General Secretariat of Commerce & Consumer Protection, took place according to information brought to the attention of SecNews.
According to reports identified by SecNews collaborators on foreign forums, unknown individuals (probably foreigners judging by the messages posted)have been adding/altering multiple websites (subdomains) for several days now while simultaneously posting a message. The hackers involved, with the aliases "Sxtz" and KuzoTR, are the ones who most likely carried out the cyberattack.
The General Secretariat for Trade and Consumer Protection has as its main objective the formulation of government policy in the field of trade, the smooth functioning of the market and the promotion of competitiveness. You can read more [here]
The websites that suffered the cyber attack
The hackers appear to have identified a possible weakness in either the website server or the content management system (CMS) at gge.gov.gr, which allowed them to gain full or partial access with privileges and add the altered content.

The altered content that has been identified up to this moment from the cyber attack and remains active is:
- On the main website of the General Secretariat of Commerce and Consumer Protection
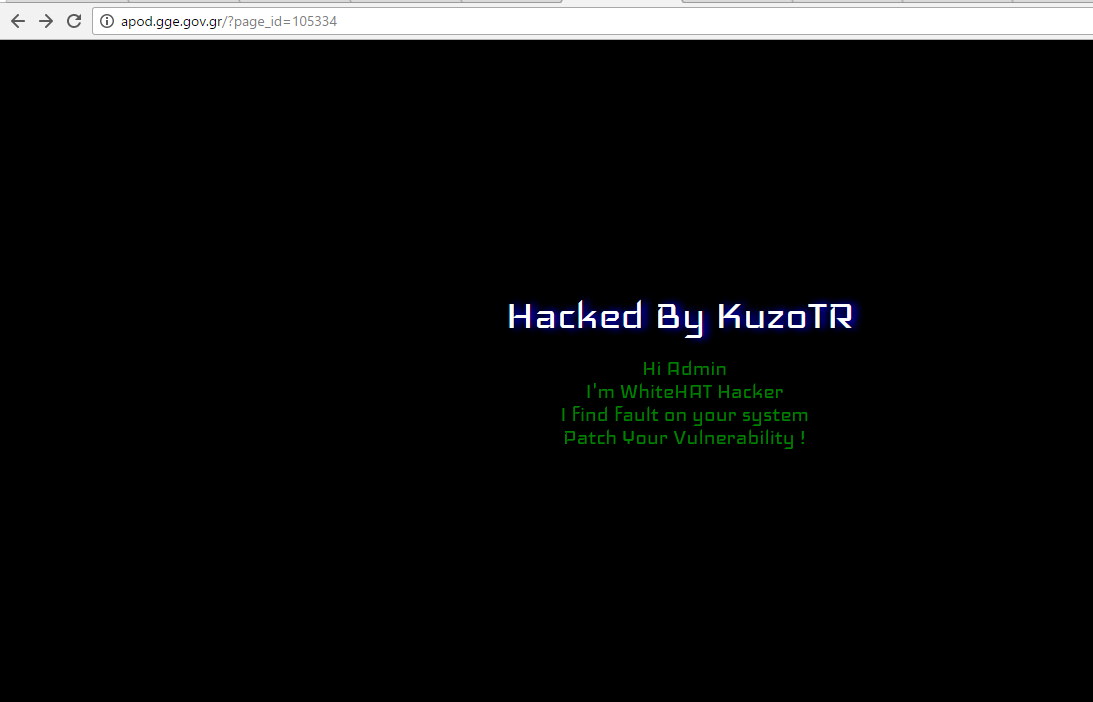
- On a subpage of the daily bulletin service https://apod.gge.gov.gr/
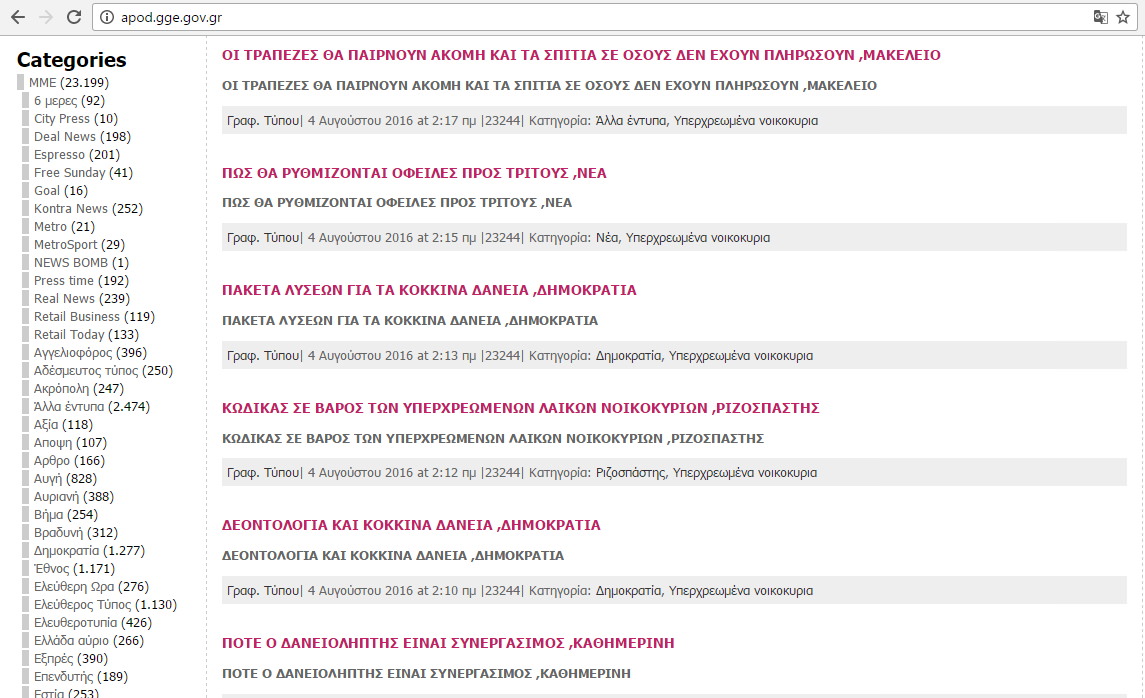
and specifically here: https://apod.gge.gov.gr/?page_id=105334
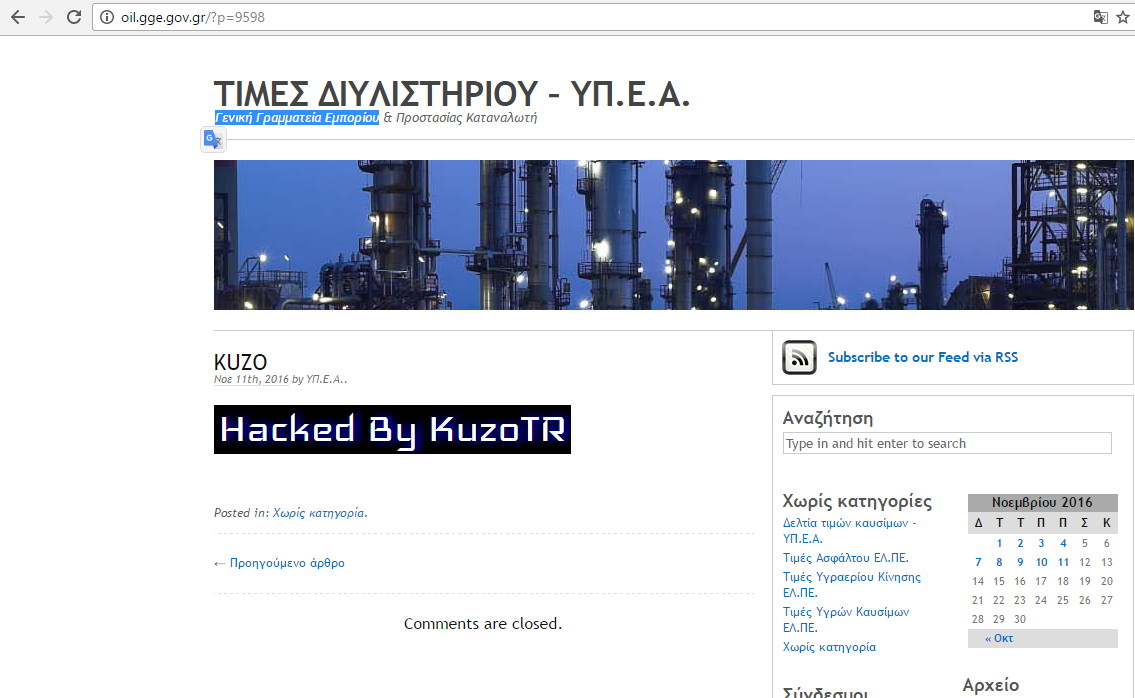
- At refinery prices / Fuel price bulletins – Ministry of Energy https://oil.gge.gov.gr/
See the alteration here: https://oil.gge.gov.gr/?p=9598
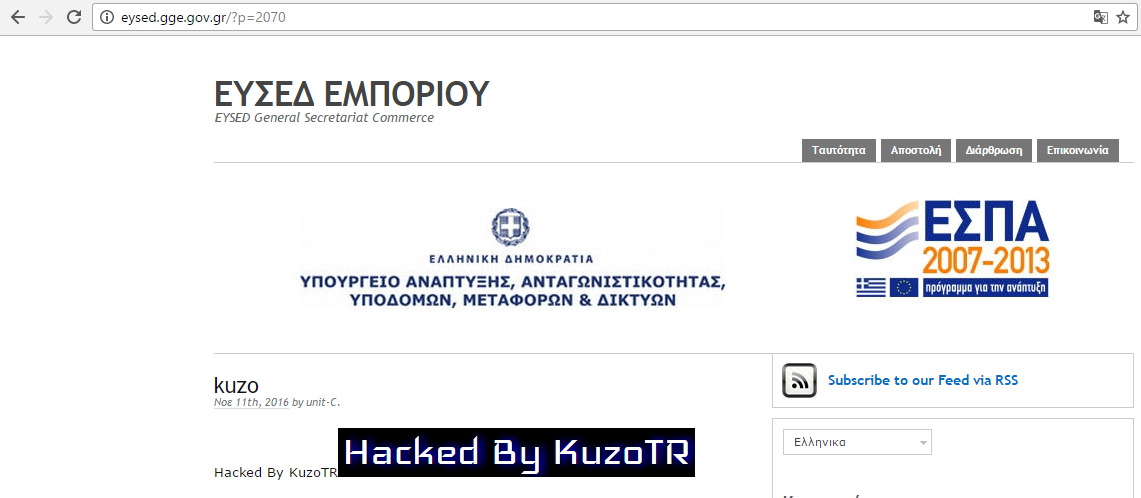
- At the Greek National Agency for Commerce https://eysed.gge.gov.gr/
Finally, a cyberattack was carried out on a subpage of EYSED here: https://eysed.gge.gov.gr/?p=2070
It is unthinkable, as security researchers who analyzed the cyber attack tell us, that government websites on the gov.gr domain constitute a playground for low‑level hackers!!! Moreover, up to now the responsible administrators do not seem to have noticed the tampering.
The information systems of the General Secretariat of Commerce that were targeted during the cyberattack, as we have found, are within the Syzefxis, which serves almost the entire Public sector, structured (at least theoretically) in accordance with all modern security requirements.
As we have mentioned many times in the past, Syzefxis as a provider DOES NOT essentially bear the responsibility of managing the servers of each entity but simply provides the means of access. Comprehensive care should be taken to ensure that at least the entities that manage sensitive personal data are protected, drawing on expertise from Syzefxis management executives who are appropriately trained and responsible for security issues.

The responsible administrators and those responsible for hosting the relevant servicesshould review or revise the security countermeasures of the websites, while strengthening the technological infrastructure so that they are able to face similar or more serious network attacks by cyber attackers in the future, should they occur.
Stay tuned to SecNews, the reliable 24-hour information website on information systems security and cyber breaches.
