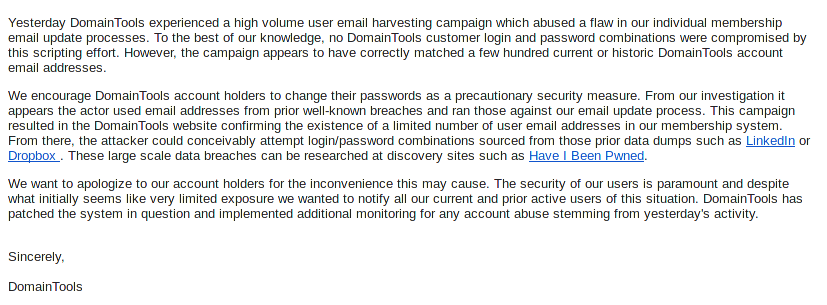
As it appears yesterday the domain name provisioning service DomainTools experienced an “email harvesting.” This attack focuses on collecting users' email of the service and according to the company the hackers exploited a flaw they discovered in the e‑mail notification processes that any user can use.
Thus the company informed all its customers, as the malicious script used by the hackers allegedly managed to collect several hundred current and even older email addresses from DomainTools accounts.
The company urges all DomainTools account holders to change the passwords they use as a preventive security measure, although, as the company notes, from the research they conducted it does not appear that passwords were leaked.
As it appears, the hacker used email addresses from earlier known breaches and ran them through the service's email notification process. In this way, he managed to confirm that DomainTools had a limited number of the email addresses used in the attack.
Naturally, the company ends the attack notification email by apologizing to the account holders for the inconvenience caused.
DomainTools reported that it has already patched the security gap and has implemented additional monitoring for any account breaches after yesterday's hack.
View the email