

According to security experts, an HTTPS hijacking click-fraud botnet named Redirector.Paco has infected nearly 1 million devices so far.
EXCLUSIVE Information that reached SecNews editors reports that a large news website with high traffic (among the 5 largest in Greece) has already fallen victim to an advanced version of Redirector.Paco and is already "serving" malware and ransomware to unsuspecting users.
Bitdefender security experts initially identified a new click fraud botnet named Redirector.Paco that has been around since at least September 2014 and has already infected over 900,000 devices since then.

The crooks behind Redirector.Paco aimed to create a clickbot that is able to redirect all web traffic that occurs when a search engine is used (for example, Google, Yahoo or Bing) and replace legitimate results with others decided by the hackers in order to earn money from the well-known AdSense.
"To redirect traffic, the malware 'tweaks' the registry a bit. It modifies the 'AutoConfigURL' and 'AutoConfigProxy' registry keys in 'Internet Settings' so that for every request a user makes, a PAC (Proxy auto-config) file will be queried. This file will tell the browser exactly where to redirect traffic to a different address," BitDefender said in a statement.
Experts highlighted the existence of certain traces that could be linked to the botnet's illegal activity, including:
- Displaying messages such as “Waiting for proxy tunnel” or “Downloading proxy script” in the browser status bar.
- Long loading time for Google page.
- The lack of characters above the number of search results pages.
The entire malware behind the Redirector.Paco botnet was bundled with installers for well-known applications, such as WinRAR and YouTube Downloader.

In one of the attacks detected, the installers contained JavaScript files that modified the “Internet Settings” registry key to change the behavior of the web browser and force it to use a proxy auto-configuration (PAC) file created by the attacker to provide fake search results. The attackers also rely on a root certificateso that any connection passing through their server specified in the PAC file appears private (encrypted) without raising the slightest suspicion from users.
“As it appears, any request to any page starting with https://www.google or https://cse.google will be forwarded to IP 93.*.*.240 on port 8484. However, at this point, the experienced user will notice that the browsing will be accompanied by a warning informing the user that there is a problem with the certificate.”

Experts also identified a .NET-based variant of the Redirector.Paco botnet that also modifies search results locally, by creating a local server without redirecting traffic to an external server.
Most infected devices are located in India, but experts have observed a high number of infections in the United States, Malaysia, Greece, Italy, Brazil and other African countries.
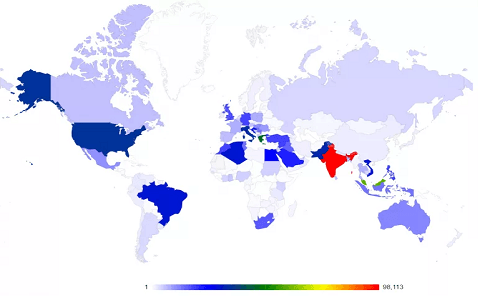
Greek users have already been infected by this malware and their computers are being used by would-be cyber gangs to extract money through Google advertising listings. SecNews invites its readers to check the above characteristics on their computers and scan them with updated antivirus IMMEDIATELY for traces of this botnet!
