

Hackers have targeted online gaming and betting companies with what appears to be an unknown backdoor that researchers have dubbed IceBreaker.

The breach method relies on sophisticated deception, aiming to trick customer service employees into opening malicious screenshots under the illusion that they have been sent by a user experiencing a problem.
Since September 2022, malicious attacks have been occurring without any clear indication of who is behind them. All that can be found are faint hints pointing to their origin.
Researchers at incident response firm Security Joes believe the IceBreaker backdoor is the work of a new advanced threat actor that uses "a very specific social engineering technique," which could lead to a clearer picture of who they are.
After thoroughly reviewing evidence from a security breach in September, Security Joes' response was faster than expected. So much so that they were able to proactively thwart three more attacks before the hackers could carry out their malicious activities .
Researchers say the only public evidence of the IceBreaker threat actor they could find was a tweet from MalwareHunterTeam in October.
Customer service scam
To deliver the backdoor, the threat actor contacts the target company's customer support pretending to be a user who is having trouble logging in or registering for the online service.
Hackers convince the support agent to download an image that describes the problem better than they can explain it. Researchers say the image is usually hosted on a fake website impersonating a legitimate service, although they have also seen it delivered from Dropbox storage.
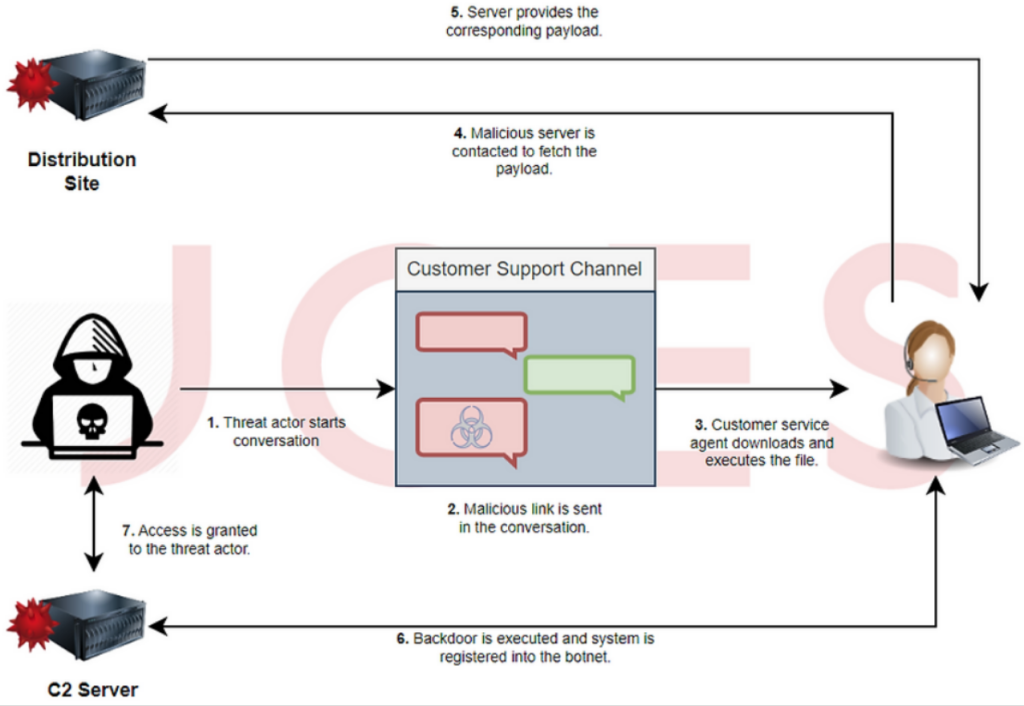
SecurityJoes says that the dialogues it reviewed between the threat actor and support agents indicate that IceBreaker is not a native English speaker and is intentionally asking to speak to Spanish-speaking agents. However, they have also seen them speaking other languages.
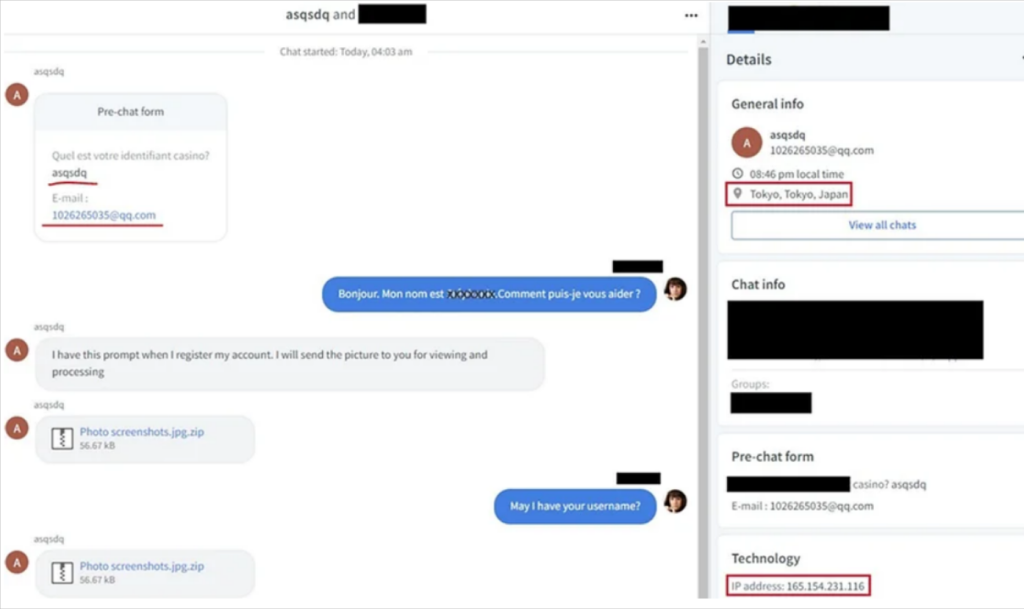
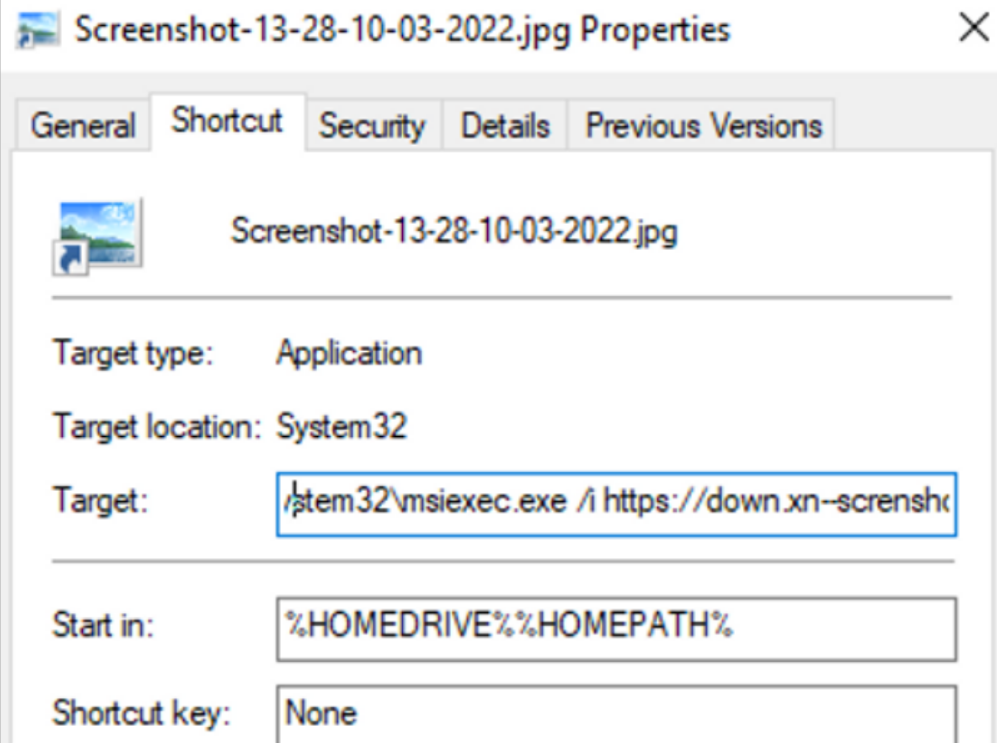
The links delivered in this way lead to a ZIP file containing a malicious LNK file that retrieves the IceBreaker backdoor or a Visual Basic Script that downloads the Houdini RAT that has been active since at least 2013.
As shown below, the Windows shortcut file icon has been changed to appear harmless. The shortcut contains a command to download an MSI payload from the attacker's server, install it without user interaction, and execute it without a user interface.
Security Joes researchers say the malware that has been downloaded is “an extremely complex compiled JavaScript” that can discover running processes, steal passwords, cookies , and files, open a proxy tunnel for the attacker, as well as execute scripts retrieved from the attackers’ server.
Information source: bleepingcomputer.com
