

A Ukrainian security researcher has leaked over 60,000 internal messages that appear to belong to the Conti ransomware gang, after the gang sided with Russia over its invasion of Ukraine.
AdvIntel CEO Vitali Kremez, who has been monitoring the Conti/TrickBot operation for the past two years, confirmed to BleepingComputer that the leaked messages are valid.
See also: LockBit & Conti: The most active ransomware in the industrial sector

In total, 393 JSON files containing 60,694 messages have been leaked from January 21, 2021 to the present. The Conti gang began their operations in July 2020, so not all conversations are included in these files.
The internal messages contain various information about the gang's activities: attacks on victims that had not been made public, bitcoin addresses, and more.
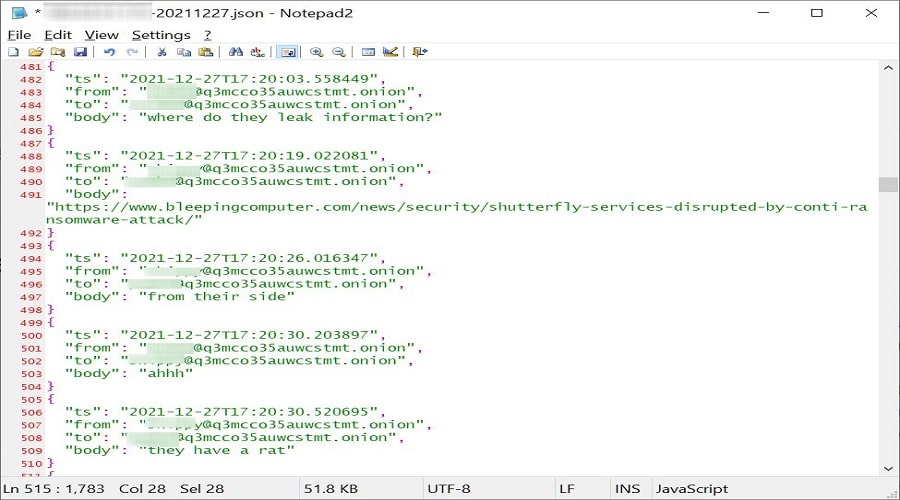
There are also discussions about Conti/TrickBot's Diavol ransomware operation and 239 bitcoin addresses containing $13 million in payments, which were added to the Ransomwhere site.
The leak of these messages is a serious blow to the ransomware business, as they have reached the hands of researchers and authorities with important information about the gang's activities.
See also: Ransomware that hit Ukraine is being used as bait
Earlier this week, the Conti ransomware gang published a post announcing its full support for attack on Ukraine. It also warned that if anyone organizes a cyberattack against Russia, the Conti gang will retaliate against critical infrastructure.

Later, the Conti gang replaced its message with another, stating that it “does not ally with any government” and that it “condemns the ongoing war.”
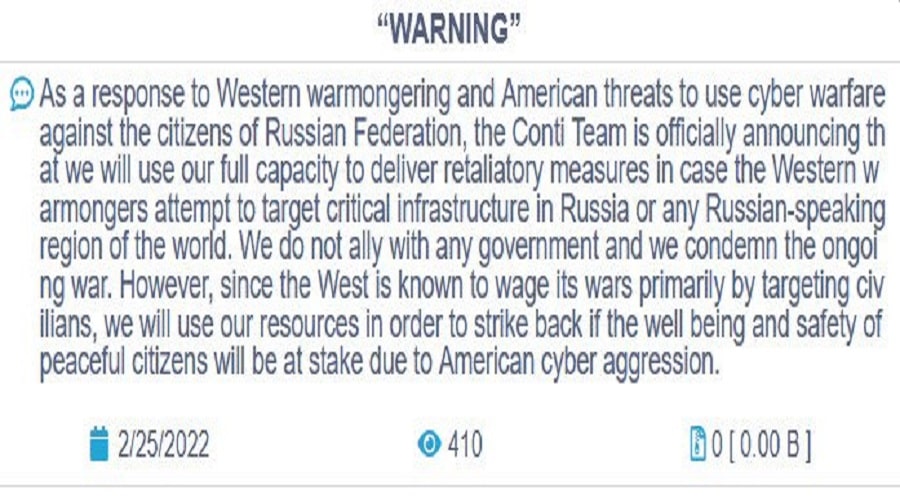
However, the initial announcement appears to have unsettled Ukrainian hackers , and a Ukrainian security researcher who allegedly had access to Conti's backend XMPP server contacted BleepingComputer and other journalists with a link to the leaked data.
Among other things, the researcher said in the message:
“The link will take you to a download of a 1.tgz file that can be unpacked by running the command tar -xzvf 1.tgz in your terminal.
The contents of the first dump contain the conversations (current, from today and in the past) of the Conti Ransomware gang. We promise it's very interesting.
More dumps are coming, stay tuned.
You can help the world by writing this as your top story.
It's not malware or a joke.
This is sent to many journalists and researchers.
Thank you for your support
Glory to Ukraine!“
The situation between Russia and Ukraine has also affected cyberspace, with many hacking groups, ransomware gangs, and researchers choosing sides.
See also: Microsoft Exchange servers compromised by Cuba ransomware
While some ransomware gangs have sided with Russia, others, like LockBit, remain neutral.
On the other hand, Ukraine has asked volunteer researchers and hackers to join its "IT Army" to carry out cyberattacks on Russian targets, with many responding to the call.
Source: Bleeping Computer
