

The Emotet botnet appears to have made a comeback. On Monday, malicious emails were sent to users in Germany, the United Kingdom, Poland, Italy, and the United States. The targets were individuals , businesses , and government entities.
In June, security researchers noticed that Emotet's C2 servers were inactive. This lasted until August 22, when they became active.
Apparently, the Emotet botnet administrators wanted some time to prepare and carry out new dangerous campaigns, hacking sites and using them to distribute the Emotet payload.
In this particular campaign, the sites that were compromised to distribute the payload are:
- customernoble.com
- taxolabs.com
- www.mutlukadinlarakademisi.com
- www.holyurbanhotel.com
- keikomimura.com
- charosjewellery.co.uk
- think1.com
- broadpeakdefense.com
- lecairtravels.com
- www.biyunhui.com
- nautcoins.com
Researchers discovered that Emotet has targeted over 66,000 emails since yesterday.
The malicious emails came from 3,362 different senders, whose credentials had been stolen.
According to the data available so far, most of the emails in this campaign are related to some financial topic. They usually appear as a response to a supposed previous discussion.
One of the malicious emails sent to English-speaking users was the following:
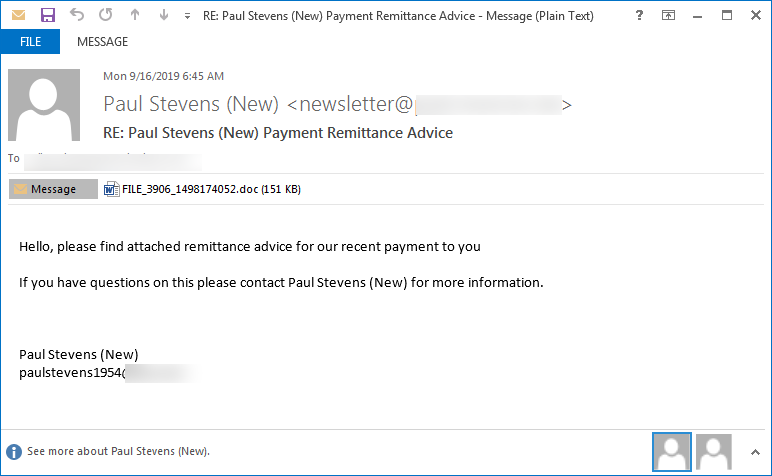
A German user received a similar email:
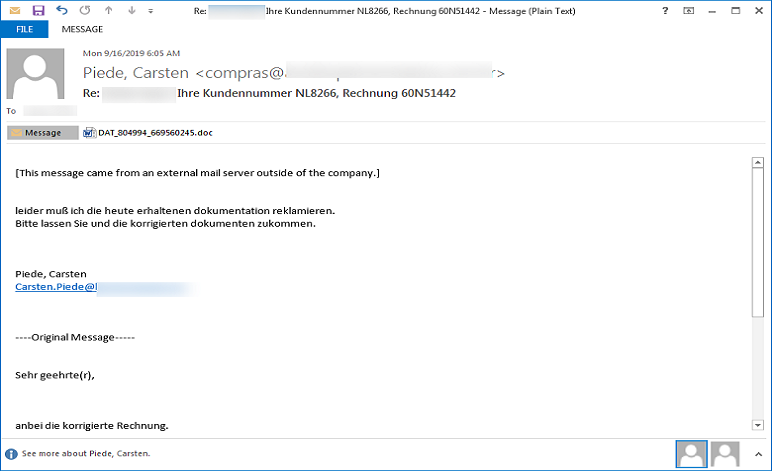
These emails appear as replies to a previous conversation. This way, potential victims are more likely to respond to the sender's request.
However, emails were also sent that did not appear as a response. For example, a US government agency received an email requesting a document review.
The common element in all emails is a financial document, which must be reviewed by the recipient.
This document is a malicious Word document through which Emotet is distributed.
The new Emotet distribution campaign has started in earnest. Security from various companies reporting new attacks.
