

Apple is currently going through a software nightmare, as the latest MacOS updates for iOS and macOS are causing a huge headache and doing more harm than good.

After users complained that the latest iOS 11.2 parses Face ID into a series of iPhone X units, it now appears that macOS 10.13.1, which was released recently, leaves the door open for hackers to exploit the critical vulnerability that was discovered last week.
Wired writes that installing this new updated version of macOS removes the updated security code version, which means that users have to reinstall it. The biggest difference is that a restart is now required to complete the installation and the vulnerability remains exploitable until the restart is completed.
While the original knowledge base article released by Apple stated that a restart was not necessary, the company has updated the advice to say that “if you recently updated from macOS High Sierra 10.13 to 10.13.1, restart your Mac to ensure the Security Update is applied properly.”
Apple recommends that users check whether the updated vulnerability code version has been installed after installing macOS 10.13.1 and provides the following steps to do so:
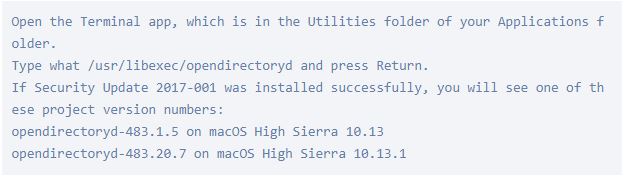
The most concerning thing is that macOS users who are unaware that version 10.13.1 reintroduces the updated vulnerable code version could leave their computers open to hacks until they develop a non-automated fix.
Apple will likely include the patch in a future operating system update to make sure all systems are fully secure, but until that happens, make sure you use the steps above to confirm Mac is protected.
