

Poseidon Group: A massive digital espionage campaign with Brazilian Portuguese as its main language and targeting financial institutions, telecommunications organizations, industrial companies, energy providers and the Media is revealed for the first time
Kaspersky Lab’s Global Research and Analysis Team has announced the discovery of the Poseidon Group, an advanced threat actor that has been conducting global cyber espionage operations since at least 2005. What makes the group behind the Poseidon Group unique is that it is a “commercial” entity, whose attacks involve custom malware, digitally signed with fake certificates, designed to steal sensitive data from victims in order to force them into financial relationships. In addition, the malware is designed to run specifically on computers running Windows in English and Brazilian Portuguese, a first in the history of targeted attacks.
At least 35 corporate victims have been identified, with the main targets including financial and government organizations, telecommunications providers, industrial companies, energy companies and other utilities, as well as media and public relations companies. Kaspersky Lab experts have also identified attacks on service companies targeting top business executives. Victims of this group have been identified in the following countries:
- USA
- France
- Kazakhstan
- United Arab Emirates
- India
- Russia
However, the dispersion of victims reportedly ends up in Brazil, where many of the victims have formed joint ventures or have business partnerships.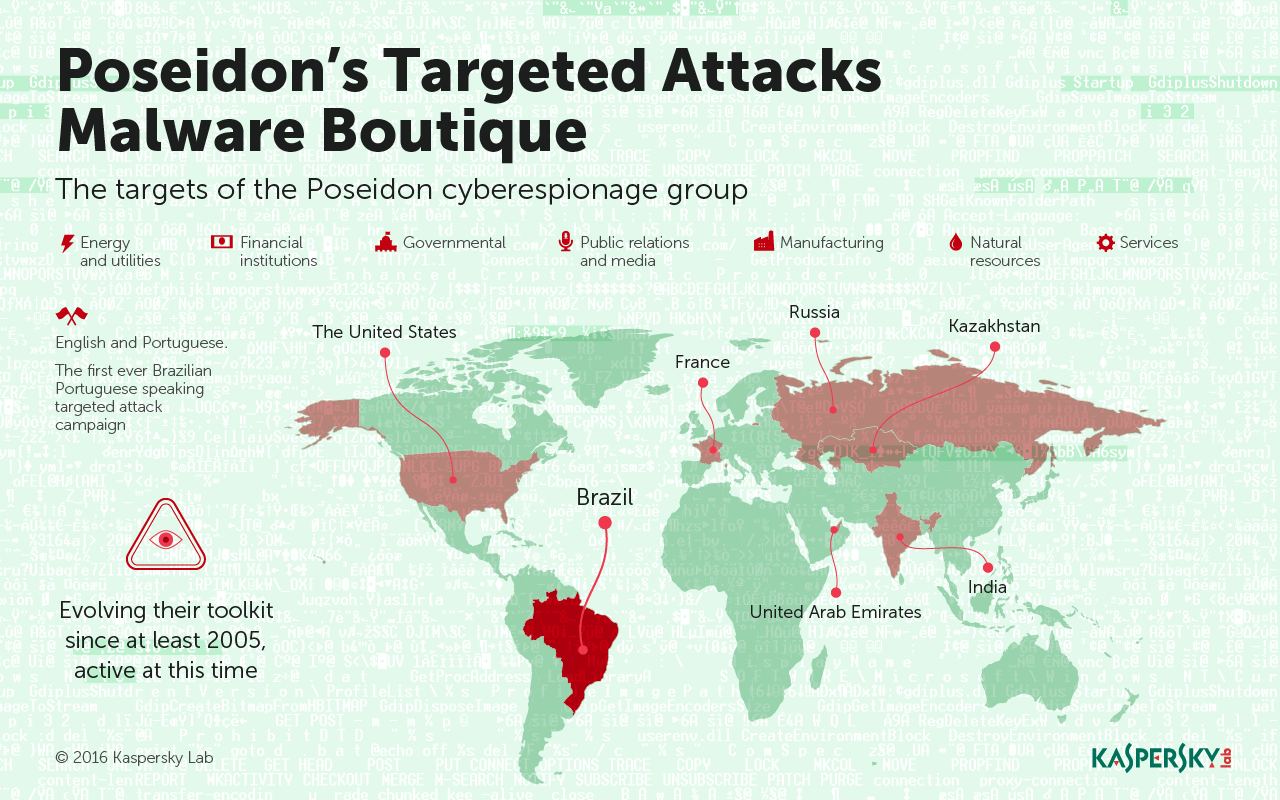
One of the characteristics of the Poseidon Group is its active exploration of domain-based corporate networks. According to Kaspersky Lab analysis, the Poseidon Group relies on spear-phishing emails with RTF/DOC files (usually using human resources issues as a lure), which “release” a malicious binary code on the target’s system as soon as they try to open them. Another important finding is the presence of the Brazilian Portuguese language. The group’s preference for Portuguese systems, as revealed by the samples, is a practice that has not been observed before.
Once a computer is compromised, the malware reports to command and control servers before embarking on a complex “lateral movement” phase. In this phase, a specialized tool is often used to automatically and aggressively collect a wide range of information, including credentials, group management policies, and even system logs, to better prepare for further attacks and ensure the malware is executed. This way, attackers actually know what applications and commands they can use, without “raising an alarm” for the network administrator during the “lateral movement” and data exfiltration processes.
The information gathered is then used by a "security firm" to convince the victim companies to hire Poseidon Group as a security consultant, under the threat of exploiting the stolen information in a series of suspicious business deals to the benefit of Poseidon Group.
“The Poseidon Group has a long history of operating in a wide range of sectors. Some of its command and control centers have been found in Internet providers that offer their services to ships at sea, wireless connections, as well as traditional carriers,” said Dmitry Bestuzhev, Director of Kaspersky Lab’s Global Research and Analysis Team in Latin America. “In addition, many of the implants they use have a very short lifespan, which has allowed this group to operate for a very long time without being detected.”
As the Poseidon Group has been active for at least ten years, the techniques used to design its implants have evolved, making it difficult for many researchers to correlate indicators and “complete the puzzle” of the case. However, by carefully collecting all the evidence, studying the threat actor’s “writing samples” and reconstructing the timeline of the attackers, Kaspersky Lab experts were able to prove in mid-2015 that traces that had been previously detected but not identified actually belonged to the same threat actor, the Poseidon Group.
Kaspersky Lab products detect and remove all known versions of Poseidon Group malware.
The full report on the Poseidon Group's activities, which includes a detailed description of the malicious tools, statistics and attack indicators, is available on the Securelist.com.
