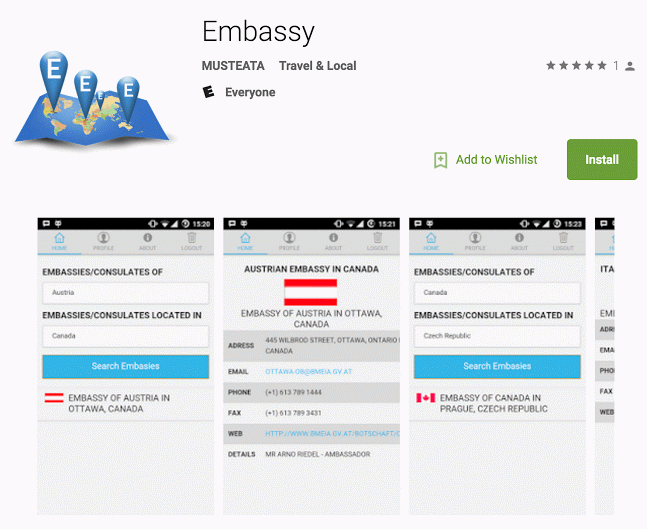
[su_heading]Google has removed four malicious apps from its online store. The apps were distributing malware to travelers who were searching for information about foreign embassies, as well as news about specific European countries.[/su_heading]
The malicious apps were named “Embassy,” “European News,” “Russian News,” while the fourth app detected was in Bosnian.
According to the researchers, all four apps were infected with the Overseer malware, which targeted travelers and mainly business executives who consulted the “Embassy” app during their business trips.
The malicious apps were discovered in late July by security experts from Security Research & Response Team. The apps were developed to collect information from victims' Android devices, including their contacts, emails, GPS data, and device information (such as the model, device ID, and whether the device is rooted or not).
As the researchers report, the malicious apps had been tens of thousands of times through Google Play.
“Through close collaboration with an enterprise customer, Lookout was able to identify Overseer, a dangerous spyware found in four Google Play apps. One of the apps was designed to help travelers find embassies abroad. The malware was also injected as a trojan into European Android news apps,” Lookout said in a blog post.
"Through the use of Facebook and Amazon services, the spyware communicates with a C&C server hosted in the United States on a popular cloud service. This allows it to remain hidden because it does not make Overseer's network traffic stand out, and its successful detection could potentially pose a challenge to traditional networked-based IDS solutions," the company continues.