

The WikiLeaks dump of emails stolen from the server of Turkey's ruling AKP party includes hundreds of links to download malware, Bulgarian security researcher Vesselin Bontchev has discovered.
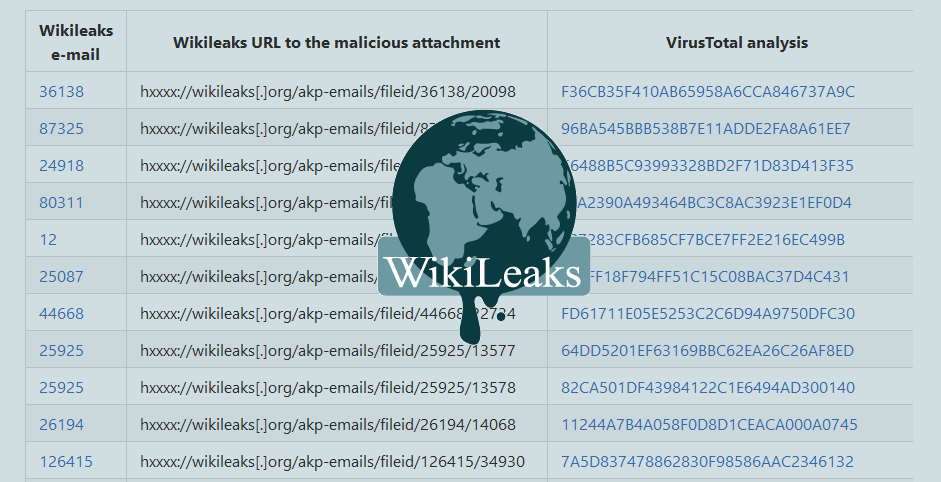
The researcher, who works at the National Laboratory of Computer Virology at the Bulgarian Academy of Sciences in Sofia, has created a script that analyzed the data of the AKP emails and sent them for scanning via the VirusTotal API.
Bontchev initially discovered about 80 links that direct to download some malware, which he presented in a report that he later modified and now lists 323 links.
The links that Bontchev’s script scanned are contained in the AKPs of emails that party members had received and were later stolen by a hacker named Phineas Fisher.
Most of them are spear-phishing emails, often ending up in RATs (Remote Access Trojans), but more often in plain malware.
Bontchev’s report includes his WikiLeaks ID, the link to the malicious attachment, and a link to a VirusTotal report.
Since mid-July, WikiLeaks has been the target of heavy criticism for its unprofessional handling of these files.
Even the hacker who managed to break into the AKP email servers to steal the data openly accused WikiLeaks of rushing to dump the files, even though he himself was not yet ready to do so and they were still on the AKP servers.
