

MICROS Systems, a division of Oracle that is one of the top three point-of-sale (POS) services in the world, was hacked by a Russian organized cybercrime group known for hacking banks and retail outlets, according to KrebsOnSecurity, a specialist cybersecurity site. According to “law enforcement sources,” Brian Krebs says the size of the hit was extremely large.

Confirming the breach to Krebs, Oracle said it had “identified and addressed the malicious code on certain MICROS systems” and was advising customers to reset their usernames and passwords for the MICROS online support portal. MICROS systems are credit card processing terminals used by banks, hotels, restaurants and hundreds of thousands of other businesses.
The breach is rumored to have been carried out by the same hacking group that stole $1 billion from banks and retailers in 2015.

While there is no warning about who the hackers were targeting in the attack, there are some indications that it may have been a cyber heist. According to Krebs' sources, the servers of the customer service portals were observed communicating with a server belonging to the Carabanak Gang, a Russian cybercrime group that stole $1 billion digitally from banks in the US and the Middle East.
It is not known when the attackers first gained access to Oracle's systems. However, KrebsOnSecurity first began investigating the incident on July 25, 2016 after receiving an email from an Oracle MICROS customer and reader who reported hearing about a potential major breach in Oracle's retail division.
According to Krebs' sources, the attack began with a single infected system that was then used as a jump-point to gain access to the remaining systems.

From there, the attackers injected malicious code into the MICROS online support portal, and this malware allowed them to steal MICROS customer usernames and passwords when customers logged into the support website. A worst-case scenario would involve malware being loaded onto customers’ POS terminals, which could be used to steal the card details of millions of customers. Currently, MICROS devices are used in over 330,000 locations in 180 countries.
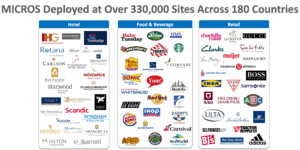
Point -of-sale systems operate at dozens of retailers, hotels and other types of merchants that have been hit by a wave of breaches over the past few years. Malware is installed on cash registers, which is then used by attackers to remotely capture payment card details when customers make purchases, which can then be used or sold to the highest bidder.
How the attack affects Greek businesses
According to data and reports, Oracle's MICROS POS systems are also used extensively in Greece in a large number of catering services, hotels and stores. Due to the powerful attack that took place, the details of which have not yet been made known, Greek companies that resell Oracle's MICROS systems are required to IMMEDIATELY inform their customers and take the relevant actions to secure the systems so that there is no leakage of credit cards.
With data from: DigitalMunition
