

Fraudsters resort to steganography and use of fileless malware to achieve their goals
US healthcare organizations represent the majority of the targeted victims of the Stegoloader Trojan, a dangerous malware that embeds its code in PNG image in an attempt to evade network and host-level detection mechanisms.
According to security experts, the largest number of infections are located in North America, affecting entities in various sectors, including financial, construction, and technology companies, as well as oil and gas companies.
Stegoloader, recently reported by Dell SecureWorks, is also known as Gatak. Its architecture is modular, meaning its functionality can be expanded to be used on a case-by-case basis, depending on the cybercriminals' goals.
[signoff icon=”icon-target”]The threat was first identified in late 2013, and since then multiple, sophisticated variants have emerged, all designed to steal information from infected systems.[/signoff]
The technique used by Trojan is called steganography, and it is commonly used in malware to update configuration files, or even to deliver malware. Although this method is not new, it is not widely used as an attack technique.
Another tactic used by trojan authors to evade detection is to execute malicious modules in the computer's memory. The PNG image or the code extracted from it and decrypted is not stored on the hard drive, leaves no trace of infection on the storage device, and evades detection through disk signature analysis.
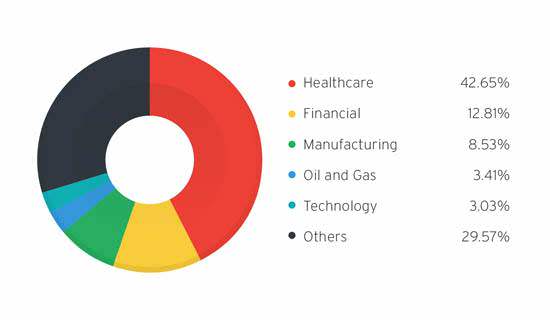
According to Trend Micro telemetry data, 42.65% of Stegoloader victims come from the healthcare sector, followed by financial sector organizations, with a percentage of 12.81%.
Homer Pacag, a security engineer at Trend Micro, believes that steganography can be used creatively in the future by cybercriminals who are exploring new ways to attack healthcare providers to steal medical data.
