

Researchers have discovered a new type of malware that infects home computers and turns them into Internet Proxies. Palo Alto Networks, the security firm that discovered this malware, believes that users' computers are being used by a Russian company through their Web Proxy service.

Named ProxyBack, this malware was first observed in March 2014, but only recently security researchers have managed to figure out how it works.
According to Palo Alto experts, the malware has infected, in most cases, educational institutions in Europe and targets public computers, turning them into Internet proxies while also using them illegally to channel Internet traffic.
The infected machines are not used to conceal the location of a cyber-scam, as security researchers explain, but to be advertised as reliable proxy servers that appear on the list of an online proxy service operating outside Russia.
The ProxyBack malware works by infecting a computer, establishing a connection to a proxy server controlled by the attackers, from which it receives instructions and then hijacks the traffic needed to redirect it to real web servers.
Every machine infected with ProxyBack functions as a bot within a larger network controlled by the attackers, who send commands and update instructions via simple HTTP requests.
Given that each infected victim has its own ID parameter in the HTTP requests it receives from the C&C server and this number gradually increases by one for each PC, Palo Alto Networks reports a count of employees in which 11,149 infected computers were found up to December 23, 2015.
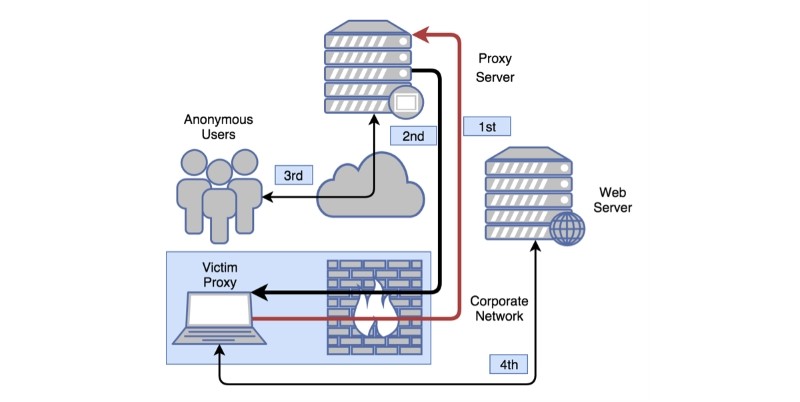
Even though the researchers did not identify any specific electronic trail to blame the domain operators, buyproxy.ru, the researchers discovered that the IPs of some infected computers appeared in their online offering, as IPs of some of their available proxy servers.
The service buyproxy.ru advertises that it operates between 700 and 3.000 proxy servers per day, that its Proxies usually live between 4 and 24 hours and a “backend proxy” is used to manage incoming connections, which then distributes to temporary proxies that have different IP addresses. This description sounds a lot like the ProxyBack malware C&C and its bots.
«Whether the people behind «buyproxy[.]ru» are responsible for the distribution of the malicious software ProxyBack or not is unknown, however, it is clear that the malicious software ProxyBack has been designed, and is used, for their service», says Jeff White of Palo Alto.
