

A critical vulnerability in the Photo Album Plus plugin for WordPress allows logged-in users with Subscriber privileges and above to cause remote code execution (RCE) on the server . The issue concerns the way ImageMagick processes the name of an uploaded file.
The new entry , CVE-2026-87909, was published on September 19 and has a CVSS score of 7.5. NVD records the RCE, while the report on CVE Feed, sourced by Wordfence, describes the issue as remotely exploitable, without documenting any public attack code.
See also: Critical vulnerability in WooCommerce Wholesale Lead Capture
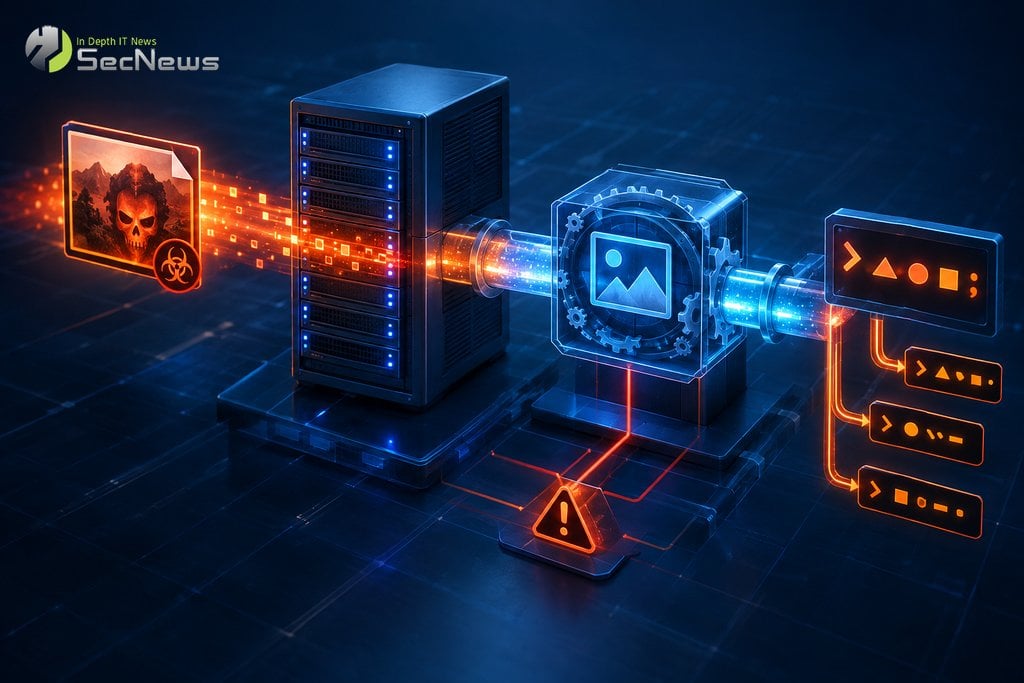
How the Photo Album Plus vulnerability works
Photo Album Plus uses ImageMagick for image conversions and processing. When a user uploads a photo, the name of the temporary file is passed to the wppa_image_magick, which constructs a command that is executed via PHP exec().
The problem is that escapeshellcmd() to the entire command, without enclosing the arguments separately. Shell characters are escaped to some extent, but spaces still act as argument separators. Thus, a specially formed filename can add parameters to the ImageMagick call.
The entry also states that the name being sanitized in the database is not the same as the physical temporary path used during processing. This creates a dangerous gap between the input control and the actual command that reaches the operating system.
Which websites are at risk from Photo Album Plus?
Versions of the add-on up to and including 9.2.09.002, according to the CVE entry. The WPScan records the fix in version 9.3.01.003 and shows around 10,000 active installations, so the issue isn't just limited to test sites.
The Subscriber account requirement limits the initial entry point, but does not eliminate it. An attacker can exploit an already compromised account, a weak sign-up process, or other vulnerability that leads to user creation. On an online store or a site with many authors, the attack surface is larger.
See also: Elementor Pro: Critical vulnerability allows RCE without authentication
Successful code execution could allow changes to WordPress files, installation of a backdoor, credential theft, or lateral movement to other services on the same server. The CVE does not document a specific exploit campaign, so technical capability should not be confused with a confirmed attack.
What should administrators do?
The SecNews technical team recommends immediately updating Photo Album Plus to version 9.3.01.003 or later, after taking a backup and checking the compatibility of the site. Administrators should confirm from the add-ons panel that the upgrade is complete and that no older file remains in the add-on folder.
At the same time, check for new accounts, suspicious images, modified PHP files, and unusual ImageMagick processes. Server and WordPress logs may show repeated uploads or requests to the image processing points. Disabling the plugin is a temporary option when the update cannot be done immediately.
In environments where the plugin is used for public galleries, administrators can temporarily restrict upload permissions and require administrator approval. This policy does not replace updating, but it does reduce the chance of a malicious filename reaching the ImageMagick feed before the restoration is complete.
It is also worth checking server settings, write permissions on temporary file folders, and the ability to run unnecessary tools from the PHP account. Segmentation, process monitoring, and backups limit the consequences if the issue is exploited before the fix is installed.
🔒 Protect your privacy with Proton VPN
Swiss VPN from the creators of Proton Mail — strict no-logs policy, strong encryption, and built-in NetShield that blocks ads, trackers, & malware.
- ✔ No-logs, based in Switzerland (except 14-Eyes)
- ✔ NetShield: blocks ads, trackers & malicious domains
- ✔ Covers all devices — free version available
The link is an affiliate link — SecNews may receive a commission at no additional cost to you. It does not affect the independence of our article writing.
See also: ImageMagick use-after-free: Critical vulnerability in FormatMagickCaption
The case illustrates why filenames should be treated as untrusted input in any processing chain. Even when the user has a limited role, a weak connection between WordPress and an external tool can turn a simple photo upload into a command execution point.
