

A new ransomware discovered by security researchers is capable of encrypting files on Windows, Linux , and macOS devices. The PureLocker Ransomware is being used by malicious actors to carry out attacks on corporate networks and servers.
According to the researchers' analysis, PureLocker is related to “more_eggs,” a malicious backdoor, often used by the Cobalt Gang and sold on the dark web.
The ransomware is written in the PureBasic programming language and can affect Windows, Linux, and OS-X systems.
The PureLocker Ransomware primarily targets Windows and Linux infrastructures, and attackers use various evasion techniques to avoid detection and the ransomware to remain undetected for several months.
Once it infects a system, the malware code begins checking to make sure the file executed as expected by its creators, and the malware is removed if any of these checks fail.
Once the malware executes its payload, it deletes itself and, using techniques to cover its tracks, leaves no evidence that would raise suspicions.
After completing the encryption, the ransomware adds the “.CR1” extension to each encrypted file and deletes the original to prevent recovery.
The ransomware then displays a ransom message on the user's desktop, called YOUR_FILES (.) Txt.
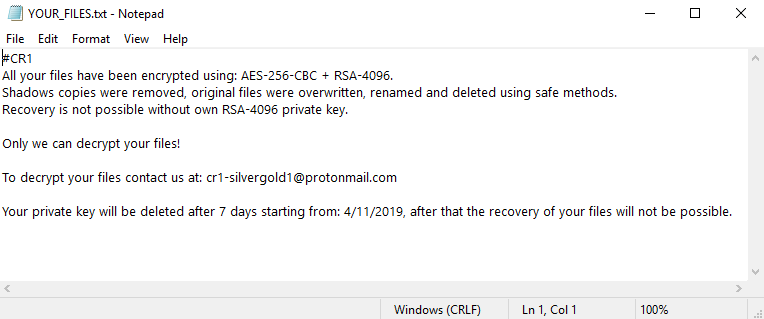
The message does not provide any payment information and simply asks the user to contact the hackers via email. For this purpose, they use the anonymous and encrypted email service Proton.
You can learn more information about PureLocker ransomware here.
