

A new crypto scam offering free Bitcoin is being advertised on scam websites offering free Ethereum.
A new crypto scam has just been discovered by an independent security researcher named Frost on Twitter. It offers $5-30 worth of free Bitcoin per day by simply running a so-called Bitcoin Collector program, but in reality, when the user clicks, it only installs ransomware or a password-stealing Trojan on the victim’s device. The scam can be advertised on scam websites that offer 3 ETH to users, telling them they will earn money every time someone clicks on the link id, such as the website ethmoney.club.
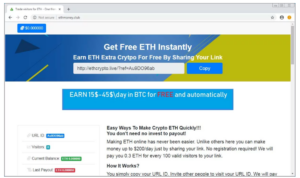
Clicking on the ad that says “Earn 15$-45$\day in BTC for FREE and automatically” will take users to another page containing a link to download the Bitcoin Collector program, which also provides a VirusTotal, presumably to show the link’s safety and enhance its credibility to ultimately convince victims to click.
Once they click, a file containing a Trojan will be downloaded, which will infect the computer after installation and automatically launch a malware payload.
In an earlier version, the payload was actually a HiddenTear ransomware called “Marozka Tear Ransomware”, which when run displays a message saying “All your information (documents, databases, backups and other files) on this computer will be encrypted using cryptographic algorithms. All files were formatted with the .Crypted extension. This “.Crypted.” file extension is a creation of American hackers. You can restore files using a decryptor and a password. It is impossible to do it any other way. Reinstalling the operating system will not change anything. No admin in the world can solve this problem without knowing the password. Under no circumstances should you modify the files. But if you want to make modifications, take a backup. Send us an email at india2lock2gmail.com. You have 48 hours left. If the files are not decrypted, after 48 hours they will be removed forever!”
According to the BleepingComputer team, the latest version is more dangerous, as the Trojan contained within it is capable of stealing the credentials of websites visited, taking screenshots, retrieving browser history, stealing files from the infected computer, and even stealing cryptocurrency wallets.
Be very careful with your clicks, this is the best advice we have to give to all crypto investors out there!
