

The browser extension of the Keybase app is unable to maintain the full encryption offered in its desktop version. Keybase is a communication and collaboration app that focuses primarily on securing source-to-destination traffic through key encryption. Wladimir Palant, creator of the popular content filtering tool AdBlock Plus, after reviewing Keybase found that messages it sends were exposed to third-party JavaScript code.
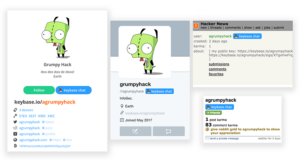
The extension adds a “Keybase Chat” button to profile pages for Facebook, Twitter, GitHub, Reddit, and Hacker News. Clicking the button opens a chat window where users can type their message. “When you compose your text and send it, the extension passes it to your local copy of Keybase, which encrypts the message and sends it over Keybase chat,” the extension’s FAQ for Chrome and Firefox. Here’s the issue Palant points out: messages aren’t encrypted until they reach the desktop app. Keybase embeds its button on web pages, but it doesn’t isolate itself from them.
“Thus, the first consequence is that the Keybase message you enter on Facebook is in no way private. Facebook's JavaScript code can read it as you type, even in end-to-end encryption”, explains Palant and suggests using an iframe to resolve this issue.
Keybase's response to Palant's proposal is that technical reasons prevented the isolation of the code via iframe.
Palant's recommendation is to uninstall the Keybase browser extension as soon as possible, especially if your personal data is included.
