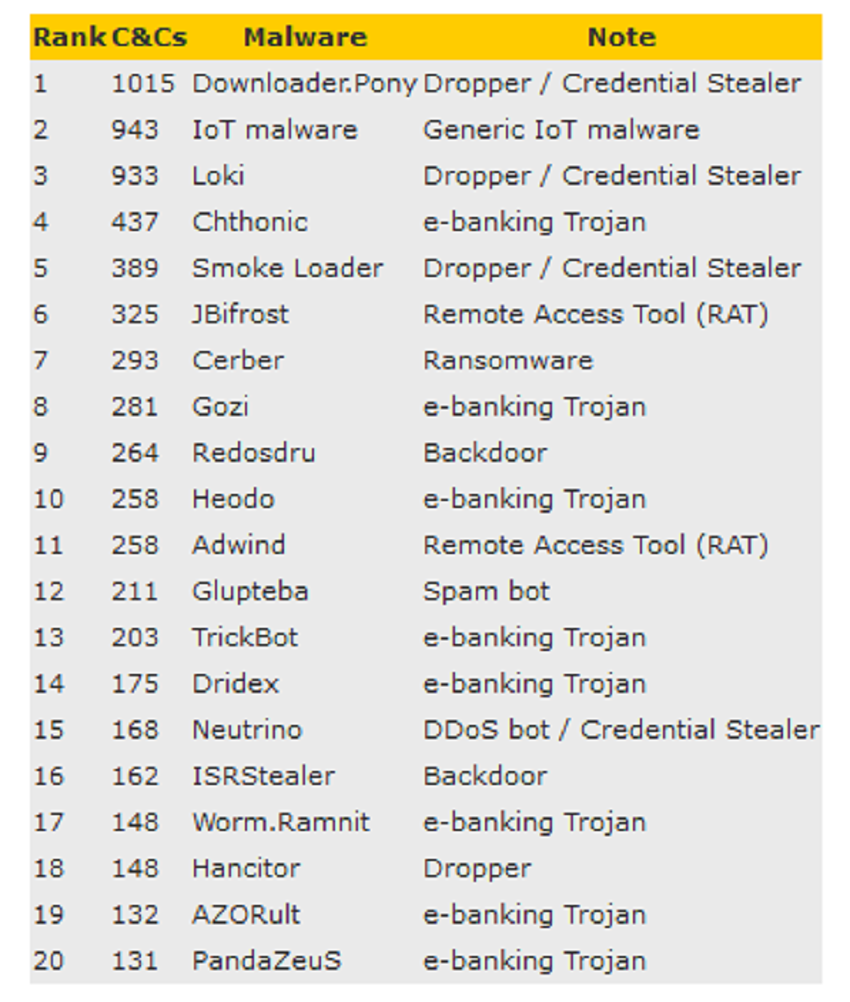
In 2017, the number of C&C servers used to manage IoT Botnets more than doubled, from 393 in 2016 to 943 in 2017.

The number is based on statistics provided by Spamhaus, an organization that compiles data on malicious websites.
In a summary report for the past year, Spamhaus says that in 2017 it uncovered over 9,500 new C&C (Command And Control) botnets, which is a 32% increase over the previous year. This statistic also includes IP addresses of botnets consisting of many types of devices, not just IoT. The 9,500+ number also includes detections of all kinds of online activity, such as C&C servers used to control botnets in DDOS attacks, spam networks, banking Trojans, and the phishing and malware kits they contain.
In addition to IP addresses, Spamhaus has also created a blacklist of domain names in cases where crooks have hidden the IP of their C&C servers behind various sites. As security researchers report, “To host botnets, cybercriminals typically prefer to use a domain name that is solely intended for the purpose of controlling them and their various operations.” According to Spamhaus, over 50,000 new domain names were recorded for C&C servers and botnets in 2017. The most common type of C&C server contained the malware “Pony,” a trojan that steals information and can collect passwords from infected devices.
Below you can see a list of the Top 20 most well-known Botnets and what type they are.