Several reports indicate that a hacker using the alias “xerub” has managed to decrypt Apple’s Secure Enclave Processor firmware (SEP) and published the decryption key on Thursday.
Apple's SEP (Secure Enclave Processor) is a component found in the A7 chipset that powers the iPhone 5, iPad Air, iPad mini 2, and iPad mini 3, as well as any A-series processor Apple has released since then.
It is capable of managing Touch ID functions , the cryptographic functions of the Apple Watch Series 2 smartwatch, password verifications, and other security-related processes.
SEP is encrypted by design and is completely isolated, meaning it cannot be compromised.
"The processor forwards the data to the Secure Enclave but cannot read it. It is encrypted and authenticated with a session key negotiated using the device's shared key provided for the Touch ID sensor and the Secure Enclave," Apple says.
The decryption key will not allow hackers to access stored data.
The hacker announced on his Twitter account that he managed to decrypt Apple's Secure Enclave Processor firmware (SEP) using the img4lib library, which can deal with img4 files, along with a SEP firmware splitting tool designed to handle the decrypted files.
Both tools were developed by the hacker and are available on GitHub for security researchers who want to try to decrypt Apple's SEP firmware to find vulnerabilities. However, these tools will not allow them to access the data stored in the SEP.
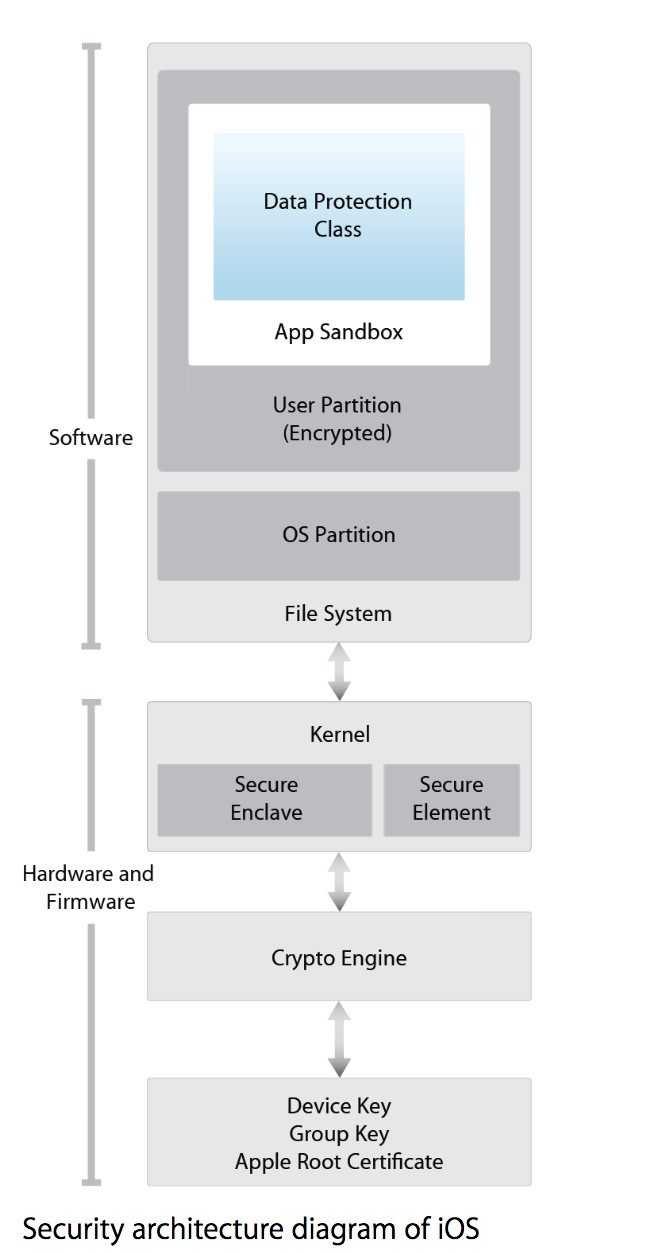
Below you can see the security architecture diagram of Apple's iOS mobile operating system to understand how its security system works. The hacker stated that the decryption key is "fully developed" and that you can download the required tools from the links below.
key is fully grown https://t.co/MwN4kb9SQI use https://t.co/I9fLo5Iglh to decrypt and https://t.co/og6tiJHbCu to process
— ~ (@xerub) August 16, 2017