

A key fact that Android users should know about their devices is that system updates come automatically and do not require the download and installation of any tool or application.

This is something that millions of users seem to have been unaware of, as in their attempt to get the latest software updates, they fell victim to a well-designed scam, downloading an Android app with spyware.
According to security researchers at Zscaler, the “System Update” app was available as a legitimate app on the Google Play Store. The app falsely promised access to the latest Android (something that, of course, cannot be achieved through any third-party app).
Most worryingly, the malicious app had been uploaded to Google's online app store since 2014, with more than 1 to 5 million downloads.
The application has now been removed from the Play Store, but it is estimated that over a period of 3 years it managed to cause great damage, infecting millions of devices with spyware.
Among the malicious application's capabilities was tracking the precise geographic location of victims (geolocation), which could be used for a wide range of malicious activities.
“The app is presented as a System Update and sending location information to third parties is not mentioned in its description,” Zscaler .
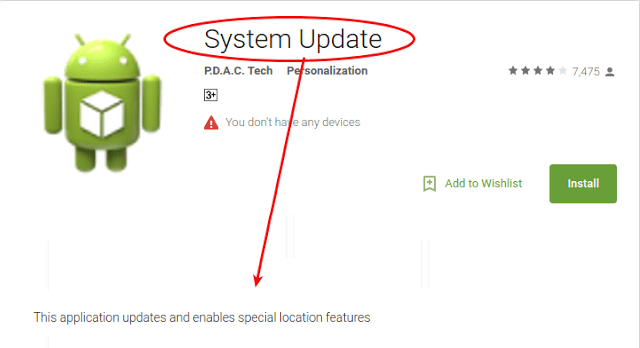
As can be seen from the comments of users who had downloaded the application, after launching it, the following message appeared: "Unfortunately, System Update has stopped", and then its operation was terminated.
This doesn't mean the app actually stopped working. Instead, the spyware created a new Android service and ran in the background, retrieving information about users' geolocation and scanning for any new incoming SMS messages.
According to the researchers, when the application detected a message with the command “get faq” (which was sent by the criminals), then the execution of an additional series of malicious commands began.
