

Operation BlockBuster Coalition reveals results of its investigation into the activities of the Lazarus Group, believed to be behind the Sony Pictures hack. The state-sponsored hackers allegedly behind the Sony Pictures hack have been linked to yet another security breach that hit a number of companies in South Korea.
The FBI blamed North Korea, the Bureau released the findings of its investigation, which showed the involvement of the Pyongyang government in the Sony Hack.
US law enforcement agencies suspect the involvement of North Korea Unit 121, which is a group of hackers working under the direction of the General Bureau of Reconnaissance.
Kaspersky Lab experts have linked the group to the hacking operations Dark Seoul and Operation Troy. According to Kaspersky, the hacking crew has been active since at least 2009 and continues to operate covertly. Kaspersky Lab, along with a number of security firms, including Novetta, AlienVault, Invincea, ThreatConnect, Volexity, Symantec, and PunchCyber, have published reports related to the activities of the Lazarus Group.
The group of security firms has formed an alliance called Operation Blockbuster, which aims, among other things, to detect and neutralize the hacking tools used by APT.
https://www.secnews.gr/
The Lazarus Group's "arsenal" includes the Destover wiper malware, the same one used against Sony Pictures Entertainment's systems.
“The group has developed multiple malware families over the years, including malware related to Operation Troy and DarkSeoul, the Hangman malware (2014-2015), and Wild Positron/Duuzer (2015). The group is known for spearphishing attacks, which include CVE-2015-6585, which is a zero-day vulnerability,” a report published on SecureList states.
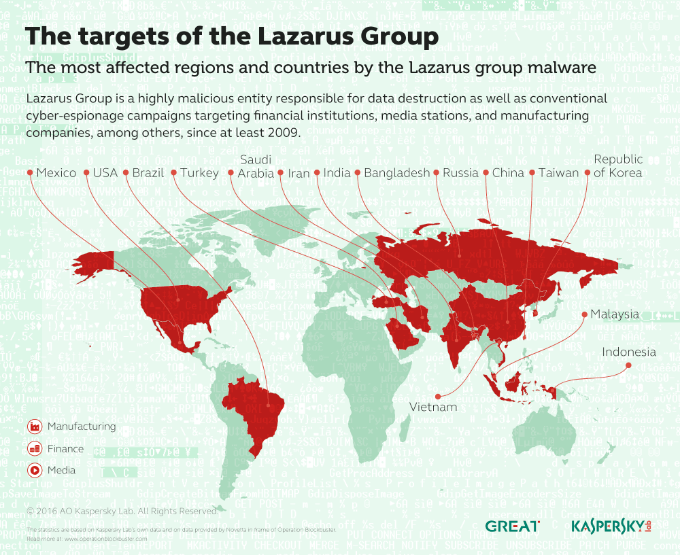
Researchers at Kaspersky Lab revealed that the Lazarus Group malware is customized and appears to be highly sophisticated.
https://www.secnews.gr/
Lazarus Group activity increased in 2014 and 2015, and the company's experts who make up the Operation Blockbuster team noticed similarities in a series of attacks around the world.
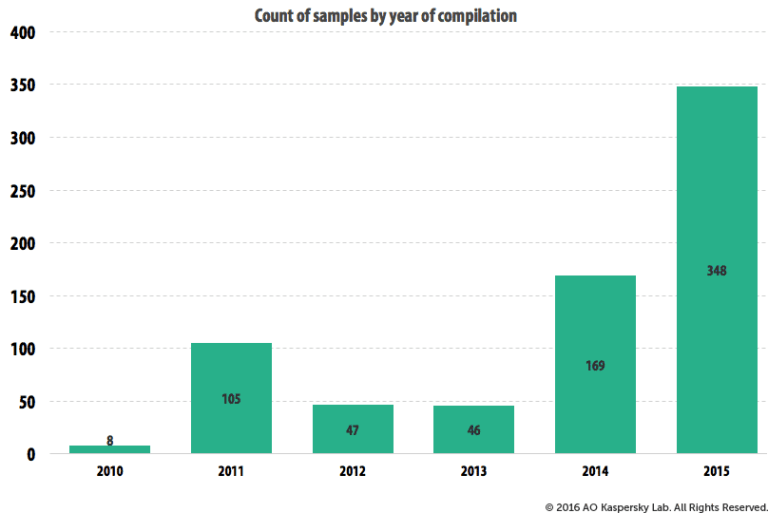
Researchers confirmed that the group is still active and is currently working on new weapons to add to its arsenal.
