

URLs in New York Times (NYT) articles published before 2013 have been found to be vulnerable to an XSS (cross-site scripting) attack, capable of transferring code to be executed in the browser.
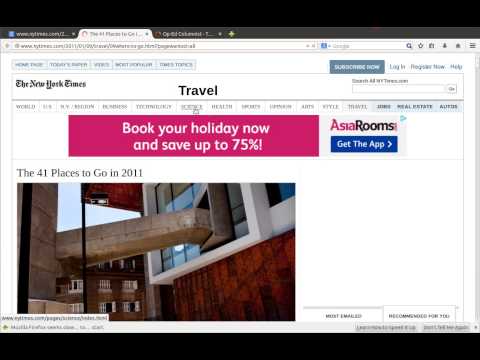
A student from Singapore named Wang Jing reported on Thursday the XSS vulnerability affecting readers of the online newspaper. He also created a video demonstrating the attack on pages of various old articles on the NYT.
An XSS stems from insufficient user input validation and allows a threat to use malicious code on those who click on the link. Basically, malicious JavaScript is added after a double-quote to a legitimate link and then executed.
The potential risk is obvious, given that the attacker could hijack browser sessions, steal cookies, or redirect the user to phishing websites.
The researcher stated that he tested the attack in Firefox (26.0), in Ubuntu (12.04) and IE (9.0.15), with Windows 7 and user login is not required, as you can see in the demonstration video below.
