

According to RSA Security, “Terracotta VPN”, a China-based VPN service provider, is powering some of the world’s most capable hacking crews, selling access to compromised infrastructure from at least 300 businesses and government agencies whose servers have been compromised through hacking.
The company, which has been dubbed “Terracotta VPN” by researchers, has more than 1,500 server nodes in China, the US and South Korea. Of these, 1,095 nodes are located in China, 572 in the US, 204 in South Korea, 27 in Taiwan and 14 in Thailand.
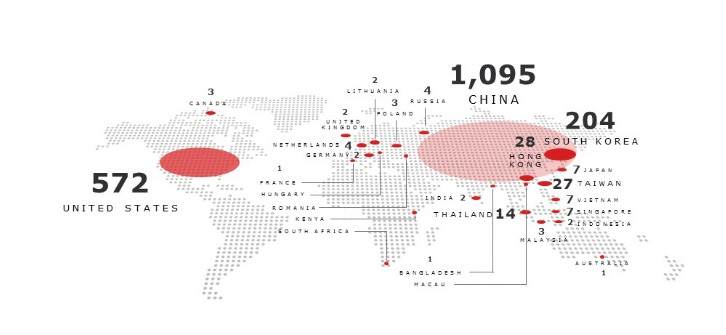
The actors behind Terracotta VPN use unfair and shady tactics to expand their services, hacking Windows-based servers and adding them to their own network.
According to the RSA report, the compromised servers include servers belonging to hotels, universities, law firms, as well as US government agencies.
Additionally, researchers analyzed how Terracotta VPN adds new nodes to its network, compromising unprotected Windows-based servers.
As RSA explains, through brute-force attacks, the attackers compromise the server administrator accounts and through them they then disable the firewall, as well as any antivirus protections, while also enabling Telnet communications. Continuing, they create their own Windows account and install a version of the Gh0st RAT (Remote Administration Tool).
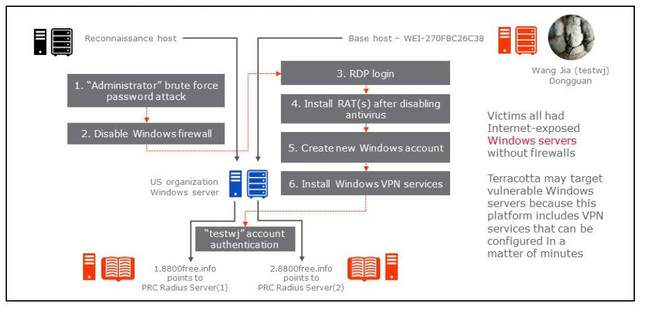
Windows Servers are also the main target of the Terracotta campaign, as they can be more easily configured as VPN nodes, compared to Linux or Mac systems.
Terracotta VPNs are used in illegal activities
According to experts, the actors behind the VPN service rent out Terracotta's network to organized APT (Advance Persistent Threat) groups, including the Chinese hacking group Shell Crew (also known as Deep Panda).
Since the company mixes malicious traffic alongside that generated by legitimate users of the VPN service, APT groups gain an additional layer of concealment of their activities.
