

Open-source software has become a fundamental part of modern technology. Millions of applications and web services rely on libraries and tools developed and maintained by communities of developers around the world. The open nature of these projects offers significant advantages, but also creates new challenges in the field of cybersecurity.
See also: WordPress adds automated plugin reviews
One of the most significant risks is supply-chain attacks, that is, attacks on the software supply chain. In such an attack, the attacker does not necessarily have to attack the end target directly. Instead, he can exploit a vulnerability or insert malicious code into a piece of software, a library, or a dependency that many other applications use.
The problem is particularly serious because a small library can be part of hundreds or even thousands of different programs. If compromised, the attack can be indirectly transferred to a large number of users and organizations. At the same time, developers often use dependencies without having a complete understanding of how they are developed, updated, and maintained.
See also: BdThemes plugins: Supply chain attack creates hidden administrators
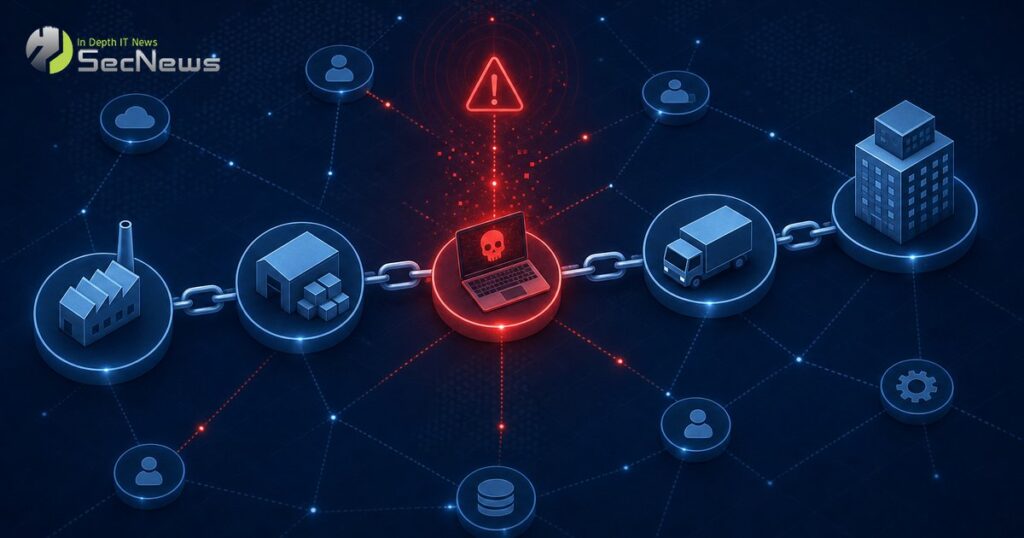
Addressing the risk requires better control of the software supply chain. Organizations can record the dependencies they use, check their origin and integrity, and install available security updates in a timely manner. Code analysis and Software Composition Analysis can also help identify known vulnerabilities.
Equally important is the security of open-source projects themselves. Using strong authentication, auditing code changes, and protecting maintainer accounts can significantly reduce the likelihood of a breach.
See also: Gemini Agent-to-Agent Attack: Leaking Secrets & Tampering with PRs
Supply-chain attacks show that the security of a system does not depend only on its own code. It also depends on all the elements that lie “behind” it. As reliance on open-source software continues to grow, protecting the entire development chain is now a basic requirement for a secure digital environment.
