

Security researchers at Russian antivirus company Dr.Web have published details of a new botnet targeting Mac OS X.
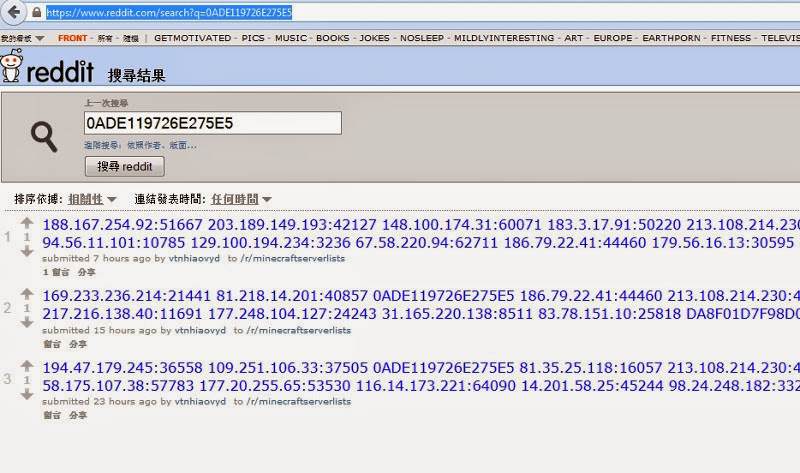
What is very interesting is that this malware uses Reddit's search function to access Command & Control (C&C) servers from comments posted in the "Mine Craft Server Lists" subreddit.
The malware calculates the MD5 hash from the current date and uses the first 8 bytes of the hash to search reddit. The result contains the server IPs with port numbers.
The malware, dubbed "iWorm," has reportedly infected over 17,000 Mac computers - 4,610 of which are in the US.
The Reddit account used by the cybercriminals appears to have been taken down. However, that won't stop the bad guys from taking control of botnet , where they either create a new account or use any other online services.
