According to security researchers at Trend Micro, routers from a well-known Chinese company contain a critical security flaw that could allow an attacker to monitor any user's traffic.
The vulnerable routers are sold in China under the Netcore brand, but also in other parts of the world under the Netis brand.
The vulnerable devices contain a “backdoor,” or a not-so-secret way to gain access to the device. The password required to open the “backdoor” is embedded in the device’s firmware, and all of the company’s routers appear to have the same password.
“Attackers can easily connect to routers , and users cannot modify or disable this backdoor,” security researcher Tim Yeh points out.
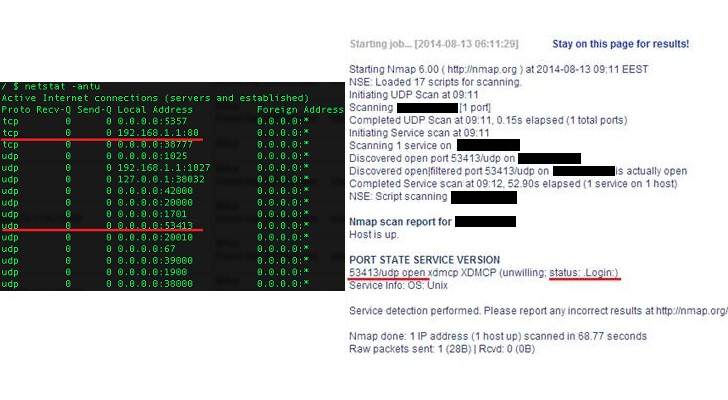
Netcore/Netis routers have an open UDP port 53413, which is accessible by any attacker if the vulnerable device has an externally accessible IP address.
Trend Micro scanned the internet and identified more than 2 million IP addresses with an open UDP port, indicating potentially vulnerable equipment.
Most vulnerable routers are found in China, with much smaller percentages in other countries, such as South Korea, Taiwan, Israel, and the United States.
Trend Micro reached out to the company about the issue, but did not receive a response.
Using the backdoor, an attacker could upload or download files to the device. It could also change a router's settings, or allow a hacker to monitor any user's internet traffic by performing a man-in-the-middle attack.