

Five security issues were identified in Siemens 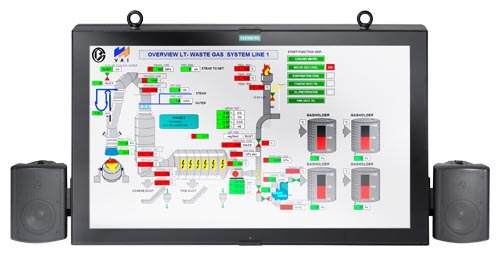 ' supervisory control and data acquisition (SCADA) system , which were fixed through a software update.
According to an advisory from ICS-CERT, the vulnerabilities are located in the SIMATIC WinCC package, and affect all versions of the software, with the exception of build 7.3.
This particular build was released by Siemens specifically to fix these vulnerabilities and can be downloaded through the company's official website
Four of the five vulnerabilities can be exploited remotely by an attacker – however only three can be used to gain administrator privileges (CVE-2014-4683, CVE-2014-4684, CVE-2014-4686).
The vulnerability with the identifier CVE-2014-4685 can also be used for privilege escalation, but requires local access to the system. Finally, the vulnerability CVE-2014-4682 can lead to unauthorized access to sensitive data via specially crafted HTTP requests.
For more information about the vulnerabilities, you can refer to the official ICS-CERT.
