

MOVEit Transfer, the software at the center of the recent massive Clop ransomware breach, has received an update that fixes a critical SQL injection bug and two other less serious vulnerabilities.
See also: Google Play: Popular file manager apps were spyware

SQL injection vulnerabilities allow attackers to craft specially crafted queries to gain access to a database or to execute code to alter it . For these attacks to be possible, the target application must lack proper input/output data sanitization.
Progress, the developer of MOVEit Transfer, discovered multiple SQL injection issues in its product, including a critical issue tracked as CVE-2023-36934, which can be exploited without user authentication
See also: Cybersecurity organizations warn of increasing TrueBot attacks
The second SQL injection flaw, identified as CVE-2023-36932, received a high severity rating because an attacker could exploit it after authentication.
The two SQL injection security issues affect multiple versions of MOVEit Transfer, including versions 12.1.10 and earlier, 13.0.8 and earlier, 13.1.6 and earlier, 14.0.6 and earlier, 14.1.7 and earlier, and 15.0.3 and earlier.
A third vulnerability addressed by this patch is CVE-2023-36933, a high severity issue that allows attackers to cause an unexpected program termination.
This flaw affects MOVEit Transfer versions 13.0.8 and earlier, 13.1.6 and earlier, 14.0.6 and earlier, 14.1.7 and later, and 15.0.3 and later.
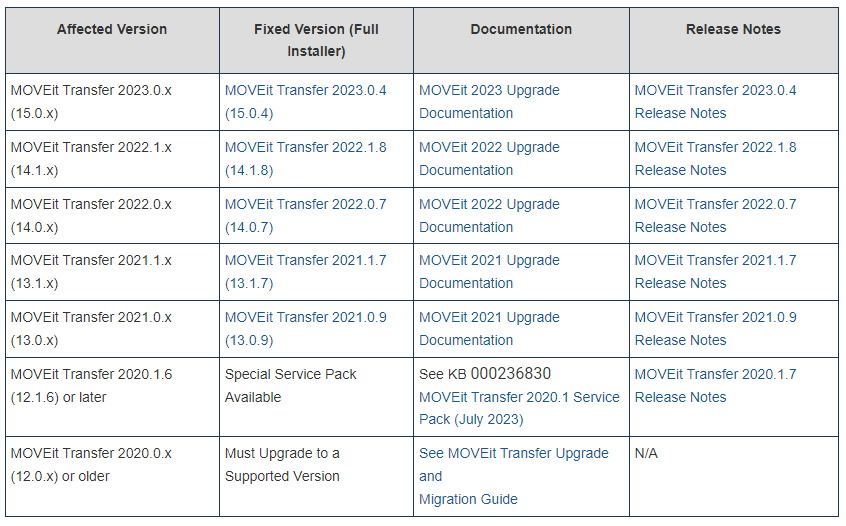
MOVEit Transfer users are advised to upgrade to the versions highlighted in the table below, which address the reported vulnerabilities.
Progress adopts security Service Packs
About a month ago, hackers – most notably the Clop ransomware gang – massively exploited a zero-day vulnerability in the MOVEit Transfer product, identified as CVE-2023-34362, to steal data from organizations around the world.
The software vendor patched the flaw a few days after it was discovered, but it was revealed that the fixes had come about two years after the hackers began exploiting it.
Progress immediately launched a security audit, which led to the discovery and repair of additional critical flaws.
See also: TA453 group targets Windows and macOS users with sophisticated malware
As the American software company continues to deal with the massive fallout from the security incident, it has decided to introduce regular security updates, called “Service Packs,” which are released every month.
As part of this new approach, the software upgrade process is being improved, allowing MOVEit Transfer administrators to apply fixes more quickly and easily than before.
Information source: bleepingcomputer.com
