

The WordPress online course plugin LearnPress has been found to have several critical vulnerabilities. These vulnerabilities in the plugin affect 75,000 WordPress sites.

See also: North Korean hackers stole millions of dollars in crypto
LearnPress is a learning management system (LMS) plugin that allows WordPress websites to easily create and sell online courses, courses, and quizzes, providing visitors with a friendly interface without requiring coding knowledge from the website developer.
The vulnerabilities in the plugin, used on over 100,000 active websites, were discovered by PatchStack between November 30 and December 2, 2022, and reported to the software vendor.
On December 20, 2022, LearnPress version 4.2.0 resolved the issues – however only a quarter of users have applied this update according to WordPress statistics.
Around 75,000 websites are potentially exposed to a vulnerable version of LearnPress – and the consequences could be dire. Exploiting this security flaw has serious potential for damage and should not be taken lightly.

Vulnerability details
The first vulnerability discovered by PatchStack is CVE-2022-47615, a local file inclusion (LFI) flaw that allows attackers to view the contents of local files stored on the web server.
Careless exposure of credentials, authorization tokens, and API keys can open the door to further infiltration.
The vulnerability is located in a piece of code that handles API requests for the website, located in the “list_courses” function, which does not properly validate certain variables ($template_pagination_path, $template_path, and $template_path_item).
By sending an API request with the intent of maliciously manipulating the three variables, a potential attacker can exploit CVE-2022-47615.
The second critical flaw is CVE-2022-45808, an unauthenticated SQL injection that potentially leads to sensitive information disclosure, data modification, and arbitrary code execution.
This vulnerability is located in a function that handles SQL queries for the website, which does not properly sanitize and validate the “$filter” variable in the query parameters, allowing an attacker to inject malicious code into it.
See also: Samsung Galaxy users should update Galaxy Store immediately
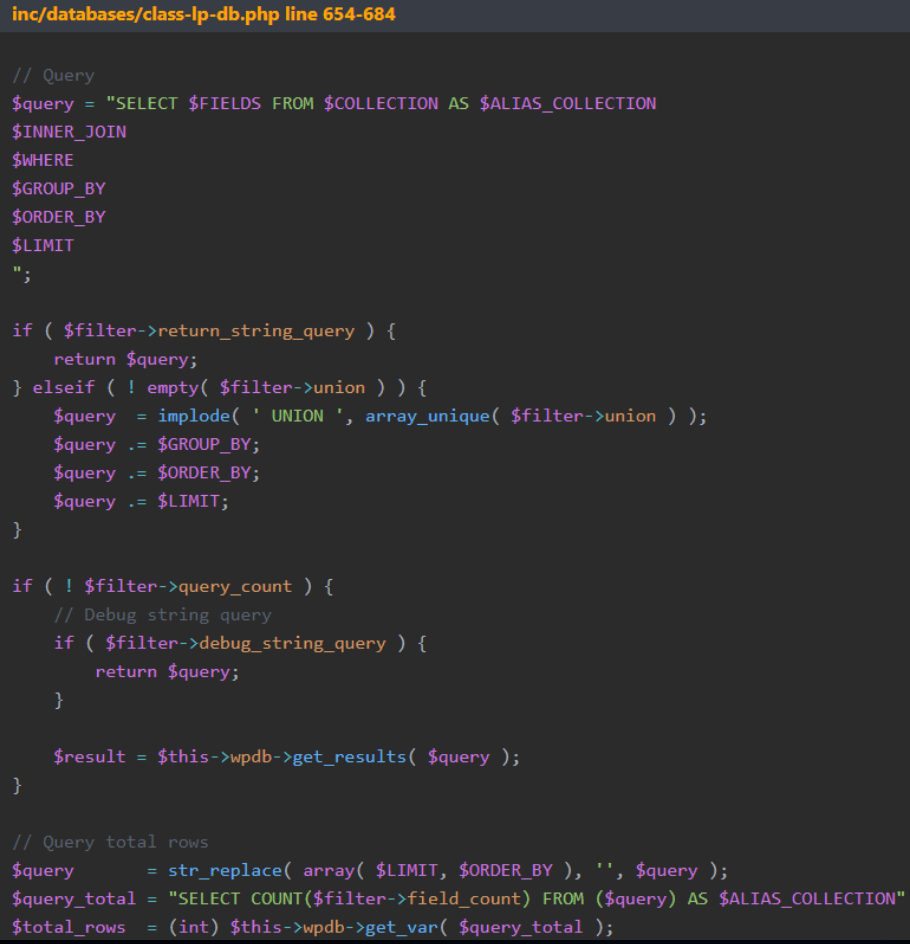
The third flaw affecting older versions of LearnPress is CVE-2022-45820, an authenticated SQL injection flaw in two plugin shortcodes (“learn_press_recent_courses” and “learn_press_featured_courses”) that fails to properly validate and sanitize the input of the “$args” variable.
PatchStack provided a proof-of-concept exploit showing how a “Contributor” user could trigger SQL injection using a specially crafted shortcode in a pre-crafted post.
To prevent this vulnerability from being exploited, it should be restricted to users with permission to create or edit blog posts. This will significantly reduce the risk associated with the flaw.
See also: GoTo: Hackers stole backups containing customer data
We strongly urge all website owners using LearnPress to immediately upgrade the plugin to version 4.2.0 or temporarily disable the program until they apply the available security update for optimal protection.
WordPress plugins offer an easy way for website owners and developers to unlock more from their websites without having to write all the code themselves. Plugins save time and money compared to coding everything from scratch, while also offering additional functionality such as e-commerce integration, contact forms, interactive elements, and more. Additionally, using up-to-date, security-focused plugins provides extra peace of mind when it comes to protecting visitor data and keeping malicious actors out of the sensitive areas of your website’s backend systems. Overall, installing some carefully selected WordPress plugins is a great way to ensure that your WordPress website is reaching its full potential!
Information source: bleepingcomputer.com
