

Zyxel has patched critical firewall flaws that could have allowed threat actors to gain full access to devices and internal corporate networks that are designed to protect them.
See also: Eternity Project: The malware kit that offers hacking tools

The company released the security updates in a silent update two weeks ago, but more details emerged recently.
Security researchers at Rapid7 found the flaw, which is now tracked as CVE-2022-30525 (CVSS v3 score: 9.8 – critical) and disclosed it to Zyxel on April 13, 2022.
The vulnerability is a remote command injection via the HTTP interface, affecting Zyxel firewalls that support Zero Touch Provisioning (ZTP). The affected firmware versions are ZLD5.00 through ZLD5.21 Patch 1.
See also: Ukrainian man jailed for selling thousands of credentials on the dark web
CVE-2022-30525 affects the following models:
- USG FLEX 50, 50W, 100W, 200, 500, 700 with firmware 5.21 and below
- USG20-VPN and USG20W-VPN using firmware 5.21 and newer versions
- ATP 100, 200, 500, 700, 800 with firmware 5.21 and below
These products are commonly used in small branch offices and corporate headquarters for VPN, SSL inspection, intrusion protection, email security , and web filtering.
Zyxel confirmed the report and the validity of the vulnerability and promised to release the remediation security updates in June 2022, however it released an updated code version on April 28, 2022, without providing a security advisory, technical details or mitigation instructions to its customers.
An exploit may appear soon
Today, Rapid 7 published the disclosure report along with the corresponding Metasploit module that exploits CVE-2022-30525 by injecting commands into the MTU field.
The researcher who discovered the flaw and developed a functional test result, Jake Baines, also published the following demonstration video.
The typical consequences of such an attack would be file modification and operating system command execution, allowing threat actors to gain initial access to a network and spread laterally through a network.
“The Zxyel firewalls affected by CVE-2022-30525 are those we usually refer to as “network core axis”. Exploiting CVE-2022-30525 would likely allow an attacker to establish a foothold in the victim’s internal network», said Rapid7 on BleepingComputer.
“From this point, the attacker can attack (or spin) internal systems that would otherwise not be exposed to the internet.”
“A real example of this type of attack would be the Phineas Fisher attack on the Hacking Team, in which Fisher exploited an internet-facing firewall/VPN.”
“Once Fisher had full access to the firewall/VPN, he was able to move laterally into internal systems (e.g. MongoDB, NAS storage, Exchange servers).
See also: Armageddon group launches new cyberattack in Ukraine
As the technical details of the vulnerability have been released and it is now supported by Metasploit, all administrators should update their devices immediately before threat actors begin actively exploiting the flaw.
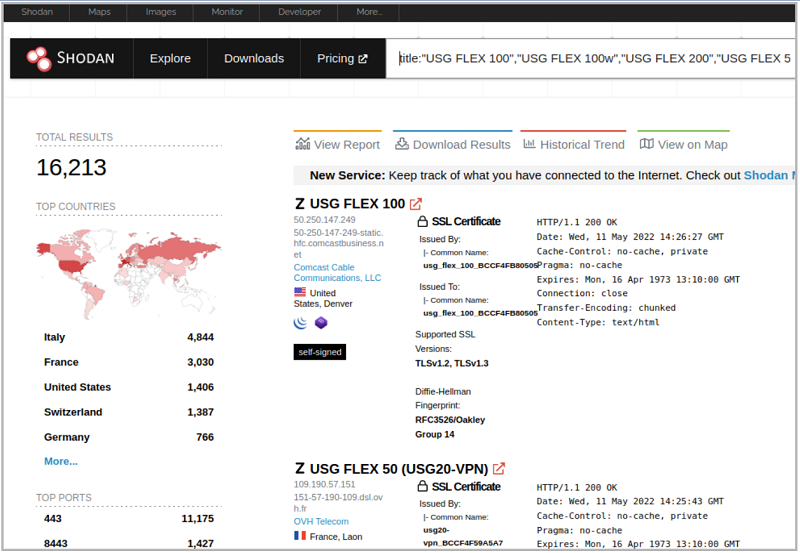
Rapid 7 reports that at the time of discovery, there were at least 16,213 vulnerable systems exposed on the Internet, making this vulnerability an attractive target for threat actors.
If updating to the latest available version is not possible, it is recommended to at least disable WAN access in the administrative web interface of the affected products.
InsightVM and Nexpose customers can assess their exposure to CVE-2022-30525 with a remote vulnerability scan.
Zyxel published a security advisory for CVE-2022-30525, attributing the lack of coordination with Rapid7 to poor communication.
Information source: bleepingcomputer.com
