

The Iranian hacking group “Agrius” has shifted from using purely destructive wiper malware to a combination of wiper and ransomware functionality – and pretending to hold data for ransom as the final stage of its attacks. In an analysis of the group’s latest moves, SentinelOne researchers said on May 25 that Agrius was first detected in attacks against targets in Israel in 2020 .
The group uses a combination of its own custom toolkits and readily available "offensive" security software to develop either a destructive wiper or a custom wiper-turned-ransomware variant.
Read also: Six ransomware gangs have "hit" 292 organizations in 2021!
However, unlike other ransomware groups – such as those of Maze and Conti – Agrius does not appear to have a purely financial motive – instead, the use of ransomware is a new addition to attacks focused on cyberespionage and destruction.
Additionally, in some attacks discovered by SentinelOne when only a wiper was deployed, Agrius claimed to have stolen and encrypted information to blackmail victims, but in reality that information had already been destroyed by the wiper.
Agrius "intentionally made its activity appear like a ransomware attack," while in reality it was carrying out devastating attacks against Israeli targets, the researchers pointed out.
The researchers also suspect that this hacking group is funded by the state.
See also: Microsoft: Massive malware campaign distributes fake ransomware!
During the early stages of an attack, Agrius uses VPN softwarewhile accessing public-facing applications or services belonging to the victim, before attempting to exploit, often through compromised accounts and software vulnerabilities.
For example, a vulnerability in FortiOS, tracked as CVE-2018-13379, has been widely used in exploitation attempts against targets in Israel.
If successful, web shells, public cybersecurity tools are used to collect credentials and network traffic, and then malware payloads are deployed.

The Agrius toolkit includes Deadwood (also known as Detbosit), a destructive malware strain. Deadwood was linked to attacks against Saudi Arabia during 2019, which were believed to be the work of APT33. Both APT33 and APT34 have been linked to the use of wipers, including Deadwood, Shamoon, and ZeroCleare.
Suggestion: Teabot: New Android malware targets banks in Europe!
During the attacks, Agrius also dropped a custom .NET backdoor called IPsec Helper for persistence and for establishing a connection to a C2 server. In addition, the group dropped Apostle.
The IPsec Helper and Apostle appear to be works of the same developer.
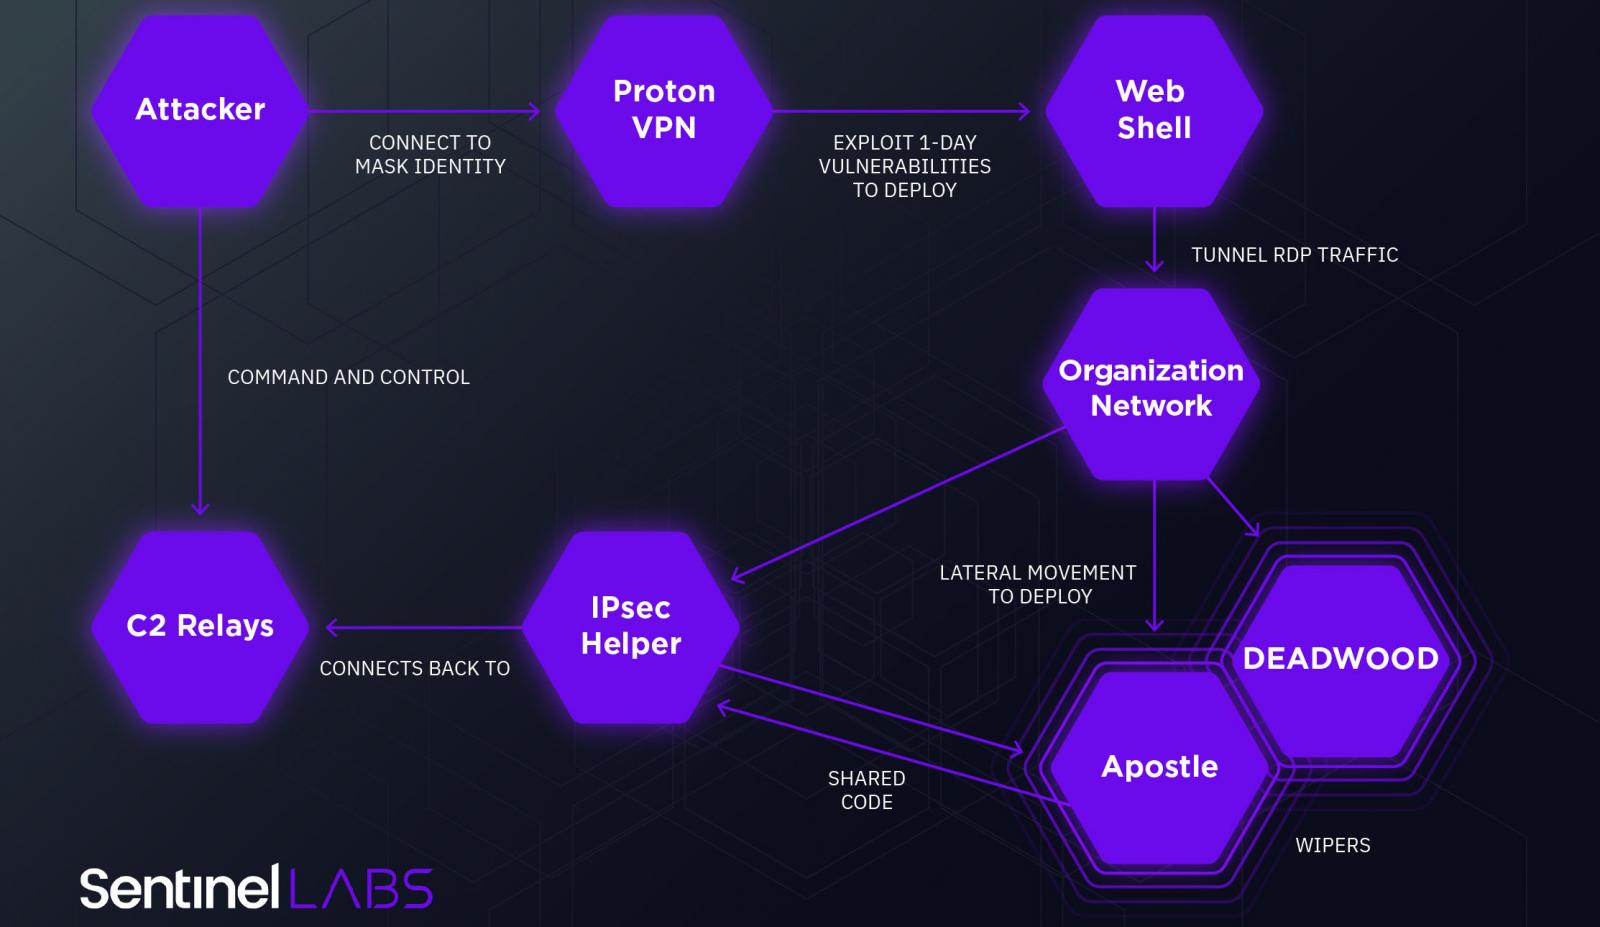
In a recent attack against a state facility in the United Arab Emirates, the Apostle appeared to have been improved and modified to contain functional ransomware components. However, researchers believe that Agrius focuses on the destructive elements of the ransomware – such as the ability to encrypt files – and not the financial lure, during development.
SentinelOne said that no “firm” connections have been made to other, established hacking groups, but given Agrius’ interests in Iranian issues, the development of web shells linked to Iranian-made variants, as well as the use of wipers (an attack technique linked to Iranian APT groups as early as 2002), are indications that the group is likely of Iranian origin.
Information source: zdnet.com
