

Security researchers have discovered that the personal data of more than 100 million Android users has been exposed due to various misconfigurations of cloud services.
The data was found in unprotected real-time databases used by 23 applications with download counts ranging from 10,000 to 10 million and also includes internal developer resources.
See also: Google Chrome: Automatically fixes compromised passwords on Android
Dozens of popular apps expose user data
While vulnerable real-time databases are not surprising, the discovery shows that some Android developers are not following basic security practices to restrict access to the app's database.
The number of mobile apps with misconfiguration issues shows that this is a widespread problem that can be easily exploited for malicious purposes.
Application developers use real-time databases to store data in the cloud and synchronize it in real-time with connected clients.
Check Point researchers found that some of these databases were left unprotected and anyone could have access to personal information, some of it sensitive, belonging to more than 100 million users.

See also: Smart home devices: Android & Google Nest get support for Matter
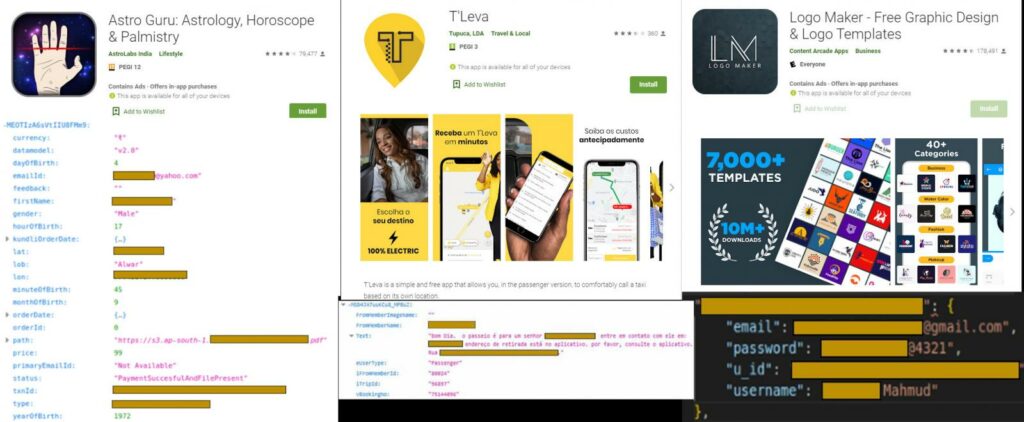
The data includes names, emails, dates of birth, messages, location, gender, passwords, photos, payment details, phone numbers, push notifications.
Some of the apps that expose this type of information are on Google Play and have more than 10 million installations (Logo Maker, Astro Guru). Others, like T'Leva, are less popular but still have a significant user base with install counts between 10,000 and 500,000.
The researchers also found sensitive details related to developers in some of the apps. In one app, they found credentials for push notification services.
In Screen Recorder, another app on Google Play with over 10 million installs, researchers found cloud storage keys that provide access to screenshots from users' devices.
They discovered that the Android app iFax was storing cloud storage keys, and the database contained documents and fax transmissions from more than 500,000 users.
See also: Android 12: Alternative app stores will update apps without disturbing the user
Of the 23 apps analyzed by Check Point researchers, twelve have more than 10 million installs on Google Play, and most of them had unprotected real-time databases, exposing sensitive user information.
While the issue is not new, it is surprising that extremely popular apps do not enforce basic security practices to protect users and their data.
Information source: bleepingcomputer.com
