

Dutch police have posted "friendly" messages on two of the largest hacking forums warning cybercriminals that "hosting criminal infrastructure in the Netherlands is a lost cause.".

The messages were published after “Operation Ladybird,” in which law enforcement agencies in various countries intervened to “take down” Emotet, one of the most dangerous botnets in the world.
The Dutch police played a key role in taking down Emotet after their officers “broke down” two of the three main Emotet command and control servers hosted in the Netherlands.
But today, Dutch police revealed that after taking down Emotet, their officers also went to Raid and XSS, two publicly accessible and very popular hacking forums, and posted messages to prevent other threat actors from abusing Dutch hosting providers to host botnets or other forms of cybercrime.
A message in English was posted on Raid, a forum popular with data thieves, and a second message, in Russian, was posted on XSS (formerly known as DamageLab), a Russian-language forum where hackers rent access to malware-as-a-service functions – a forum commonly frequented by today’s top ransomware gangs.
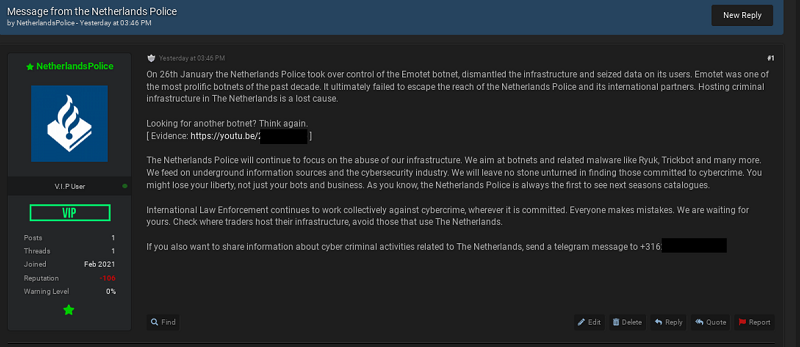
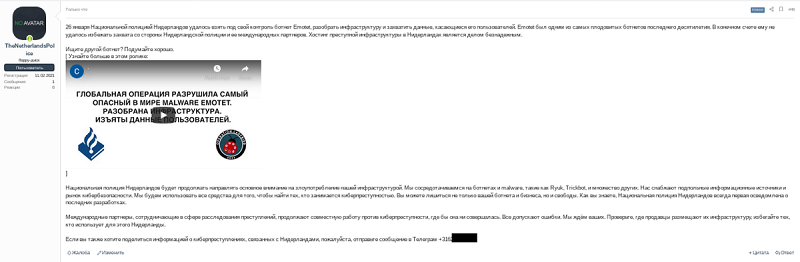
The messages, as seen above, warn hackers that “hosting criminal infrastructure in the Netherlands is a lost cause” and that Dutch police intend to continue “bringing down” infrastructure .
A link to a YouTube video was also included, a video that ends with a message from Dutch police saying: “Everyone makes mistakes. We are waiting for yours.”
The aggressive messages come as no surprise, at least to cybersecurity experts ,most of whom are well aware of the aggressive stance of the Dutch police.
Information source: zdnet.com
