

An Iranian APT hacking group called “Fox Kitten” has been linked to the Pay2Key ransomware, which recently began targeting organizations in Israel and Brazil, according to a report by threat intelligence firm ClearSky.
According to the report published on December 17, this campaign is part of the ongoing rivalry between Israel and Iran, with the most recent wave of attacks causing significant damage to some of the companies affected.

The Iranian-backed hacking group “Fox Kitten” (codenamed Parisite by ICS cybersecurity firm “Dragos”) has been active since at least 2017 and is known for orchestrating and participating in online espionage and data.
Fox Kitten also provides access to compromised corporate networks to another Iranian hacking group, called “APT33,” also known as Elfin and Magnallium. Pay2Key is a relatively new ransomware operation that has targeted Israeli and Brazilian organizations in the past month. Starting in October 2020, Fox Kitten has been using the Pay2Key ransomware in its attacks to steal sensitive and confidential data from industrial, security, and logistics companies. The group has exploited vulnerabilities in Pulse Secure, Fortinet, F5, and Global Protect VPN products or publicly exposed Remote Desktop Protocol (RDP) to gain access to targets’ networks and deploy malware payloads.
According to Check Point, the ability of Pay2Key operators to spread ransomware across a target's entire network within an hour suggests that the hacking group is likely a state-owned enterprise with APT-grade skills and resources.
The group's hackers also created a rotating device to be used as an outbound proxy server between the infected devices and the command-and-control servers , which helps them avoid or reduce the risk of detection before encrypting all network systems they access.
Indicators of compromise (IoCs) detected during the Pay2Key ransomware attacks also link them to previous devastating Iranian attacks , according to Israeli cybersecurity firms Profero and Security Joes .
Another piece of evidence that Fox Kitten is focused on information theft with Pay2Key is that the group has not even deployed ransomware payloads on the networks of recent victims, but instead only used the stolen data to blackmail the victims.
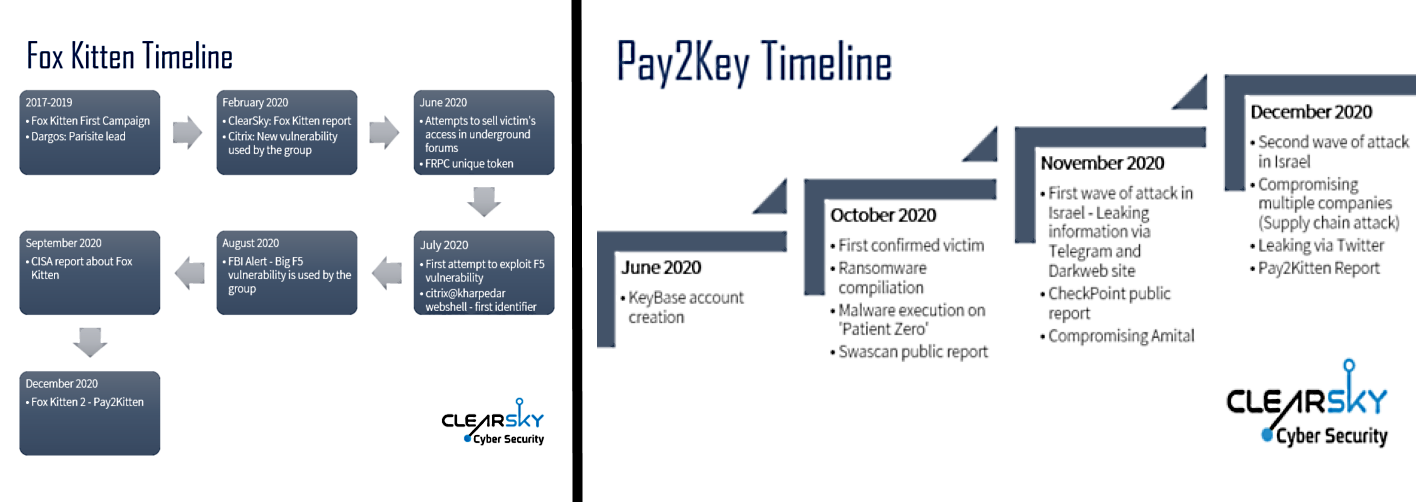
Israeli media reported that hackers breached Israeli company Amital earlier this month and then compromised 40 of the company's customers in a supply chain attack.
Additionally, as BleepingComputer reports, the hacking group known as “BlackShadow” is behind a cyberattack that occurred against the Israeli insurance company “Shirbit”, and demanded $1 million to not leak the stolen data.
While the attack that compromised Shirbit's systems is similar to the Pay2Key attacks, it is not yet known whether they are connected, as ClearSky researcher Ohad Zaidenberg reported to BleepingComputer.
Israeli cybersecurity believe these attacks have escalated due to the recent assassination of an Iranian nuclear scientist.
