

Researchers at security firm IoT Sternum have discovered three vulnerabilities in MyCareLink Smart 25000 Patient Reader that could be exploited by hackers to control cardiac devices. Designed to receive information from a patient’s implanted cardiac device , the MCL Smart Patient Reader sends the data to network to facilitate care management via the patient’s mobile device.
Hackers could exploit these vulnerabilities to modify or reconstruct data transmitted from implanted cardiac devices to the CareLink network. In addition, they could remotely execute code on the MCL Smart Patient Reader and take control of a cardiac device. To exploit these vulnerabilities, however, hackers would need to be within Bluetooth range of the vulnerable product.
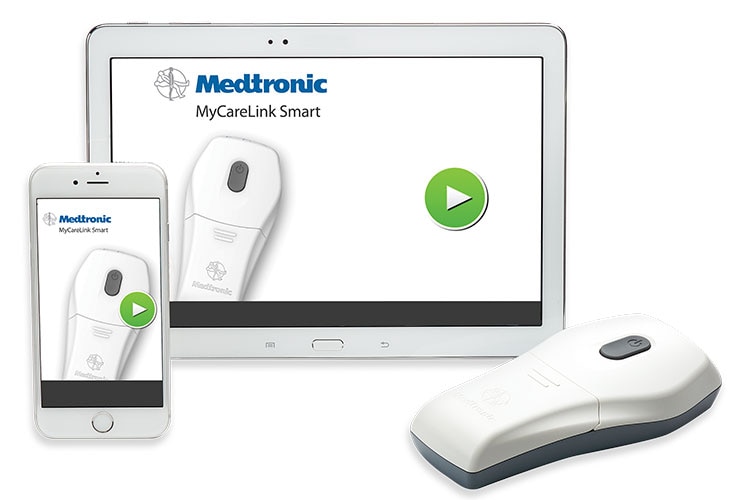
The first vulnerability , identified as CVE-2020-25183 and rated 8/10, is an authentication that allows an attacker to bypass the method used for authentication between the MCL Smart Patient Reader and the Medtronic MyCareLink Smart mobile app.
CISA says in an advisory that this vulnerability allows an attacker to use another mobile device or malicious application on smartphone to authenticate to the patient's Medtronic Smart Reader, "tricking" the device into communicating with the genuine Medtronic smartphone application, when running within Bluetooth.

The second vulnerability , identified as CVE-2020-25187 and rated 8.8/10, is triggered when an attacker executes a debug command sent to the Patient Reader. This could allow remote codeand take control of the device.
The third vulnerability , identified as CVE-2020-27252 and also rated 8.8/10, could be exploited to upload and execute unsigned firmware on the Patient Reader product. This could allow an attacker to remotely execute code and take control of the device.

Medtronic has already released a firmware update to address the vulnerabilities, which can be applied through the MyCareLink Smart app, via the relevant mobile app store. Updating the app (to version 5.2.0 or later) also ensures that the Patient Reader is automatically updated the next time it is used. The company also published detailed instructions on how to apply the update.
As additional mitigation steps, Medtronic has implemented technology and advanced detection system technology, which allows it to detect vulnerabilities and monitor anomalies in device activity.
Finally, Medtronic pointed out that no unauthorized access to patient data and no harm to patients has been observed as a result of these vulnerabilities to date.
