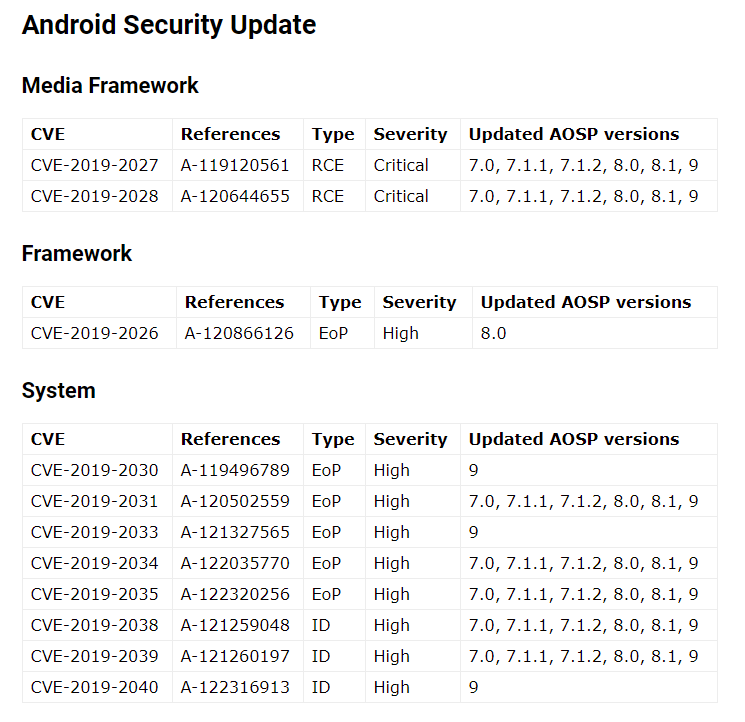
The Android Security Bulletin has released new security updates with fixes for critical vulnerabilities affecting Android devices.
The bulletin addresses two remote code execution vulnerabilities that could allow hackers to remotely run code to take control of vulnerable Android devices, although these two critical vulnerabilities affect all Android 7.0 or later devices.

Google has fixed 11 vulnerabilities that include two remote code execution issues affecting the media framework with a “critical” severity and 9 “high severity” vulnerabilities that exist in the system and the Framework.
CVE-2019-2027 and CVE-2019-2028. Two remote code execution vulnerabilities allow a remote attacker to run arbitrary code using a specially crafted file within a privileged process.
CVE-2019-2026, High severity vulnerability affecting the Android Framework allows a local attacker to gain additional privilege override with the user interface.
Another 8 high-severity system-level vulnerabilities allow a local malicious application to execute arbitrary code within the context of a privileged process.