

Warning if you are using Google's web browser, as hackers have found a new way of serving malware via Chrome. Security researchers discovered a new scam that uses Chrome. The scammers ask users to download a «missing font» and instead serve malicious software.
The scam was first highlighted by Mahmoud Al-Qudsi from cybersecurity firm NeoSMART Technologies, who detailed the attack on blog .
The researcher initially noticed the trap while browsing a WordPress site that appeared to have been compromised. Unlike other attacks, this one seemed to be very well disguised.
The hackers heavily used JavaScript to interfere with the rendering of the text, resulting in it appearing as incorrectly encoded text. The hackers' script then asked users to fix the issue by updating the “Chrome font packages”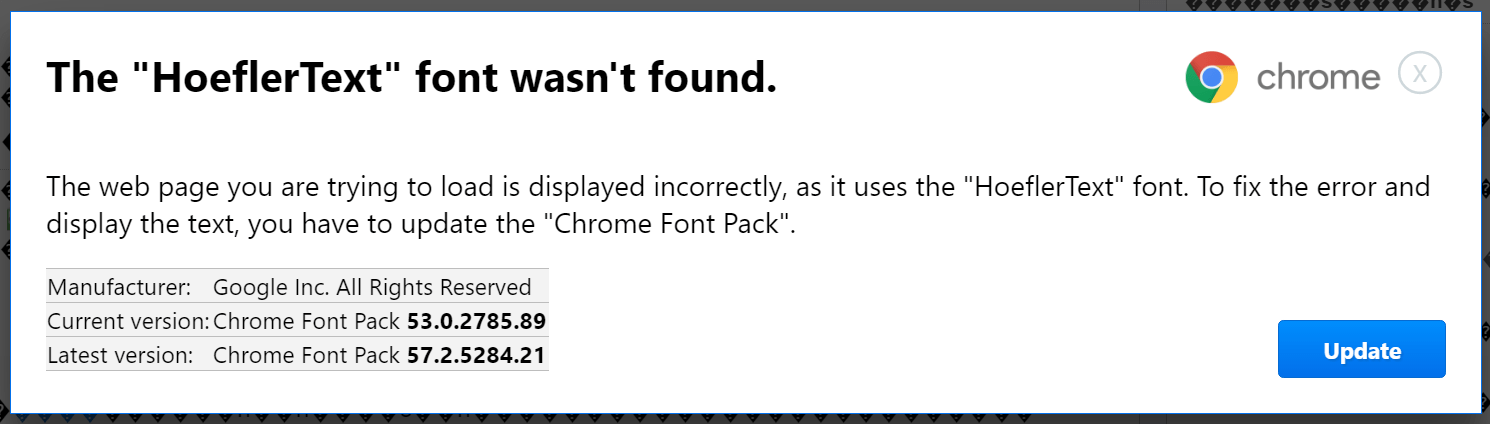
What makes the attack especially cunning is that the hacker or hackers who designed it paid close attention to appearance: the dialog box was designed to look exactly like real Chrome notification windows.
As reported by NeoSMART Technologies, there are some “indicative signs” that could signal “red flags” to careful users. One, the dialog window is hard-coded to show version 53 of Chrome, which could raise suspicions among users who are using a different browser version.
Additionally, while clicking on «Update» you should download a file titled “v7.5.1.exe Chrοme Font”, which does not match what appears in the “Crome” window that refers to it as “Chrome_Font.exe.”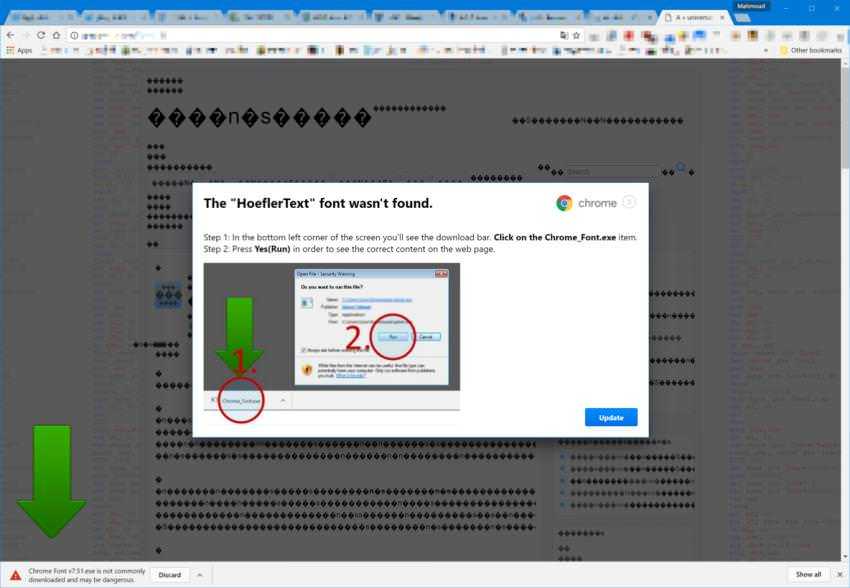
Researchers warn that Chrοme still does not filter the file as malicious software just like Windows Defender.
The security firm ran the malware on VirusTotal, and currently only nine of the 59 anti-virus scanners in the service's database have detected the file as malicious.
