

ESET 32 presents Operation Potao Express, an extensive analysis of the cyberespionage group behind the Win/Potao. 
An report ESET of the same name records all the technical details and describes the spread mechanisms and the most notable attack campaigns from the moment the malware in 2011 until today.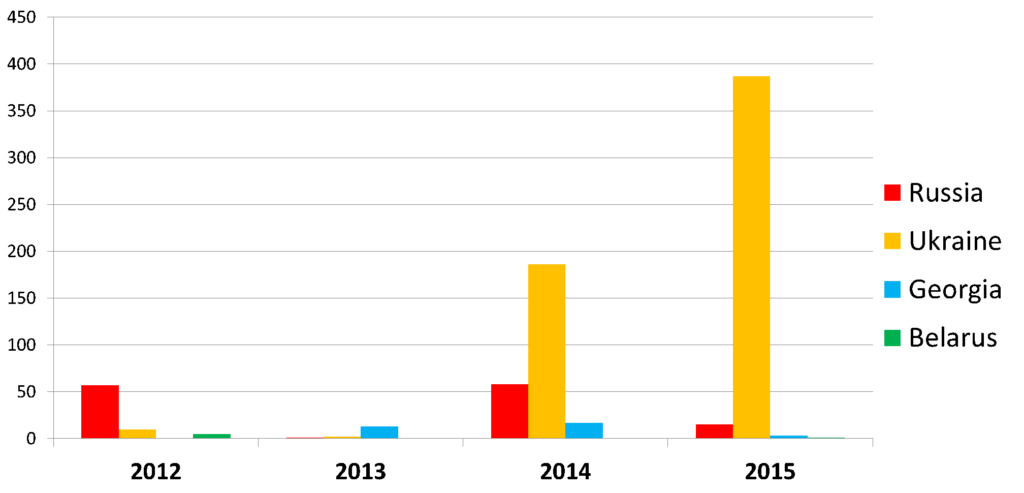
Win is32/Potao is an example of spyware. It was detected mainly in Ukraine and some other CIS countries, including Russia, Georgia, and Belarus. The Potao family a typical Trojan that steals passwords and sensitive data, sending them to the remote server that initiated the attack. 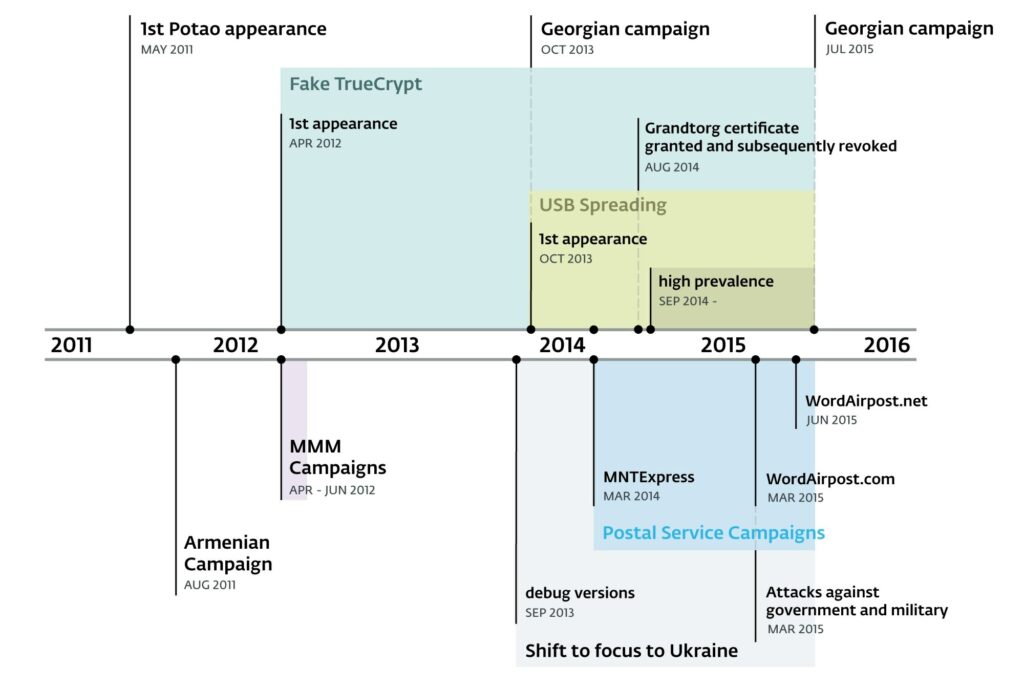
Similar to BlackEnergy, Potao was used to spy on the Ukrainian government, military entities, and a Ukrainian news agency. It was also used to spy on members of MMM, a popular pyramid scheme in Russia and Ukraine.
Beyond the variety of attack campaigns, there is another interesting fact about Win32/Potao.
“Our research into Potao revealed a very interesting connection to a Russian version of the popular open source encryption software TrueCrypt, which is no longer working,” says Robert Lipovsky, Senior Malware Researcher at ESET.
Continuing the search, ESET researchers discovered another connection between the modified version of TrueCrypt in the Trojan and the website truecryptrussia.ru , which, in addition to being a carrier of infected encryption software, was also found to be acting as a command and control ( C & C ) server for the backdoor .
More information at the link: "Operation Potao Express: Analysis of a cyber-espionage toolkit" at WeLiveSecurity.com.
