

A warning from the vBulletin informs its customers that there is a security vulnerability in vBSEO, a sub-application for search engine optimization. Administrators are advised to choose a different tool for SEO work.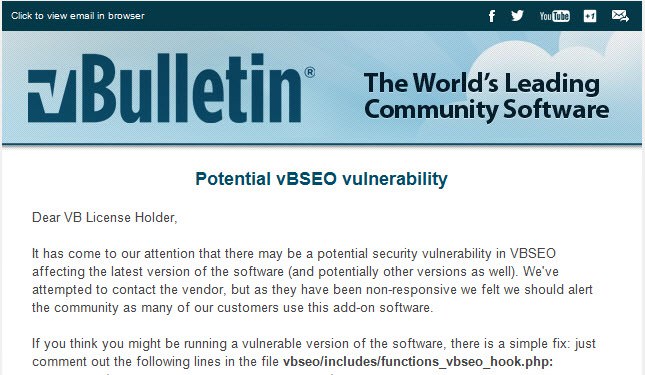
Admins, awaiting an update that will fix the issue, are informed by vBulletin that there is a solution for the problem. It consists of disabling two lines of code within vBSEO/includes/functions_vbseo_hook.php.
These two lines are as follows:
// if(isset($_REQUEST['ajax']) && isset($_SERVER['HTTP_REFERER']))
// $permalinkurl = $_SERVER['HTTP_REFERER'].$permalinkurl;
If you are also running the Suspect File Versions diagnostic tool, you will need to generate a new MD5 for the file you have modified.
However, vBulletin warns email proposing the above modification that it makes no guarantee that exploitation of the security flaw (also referred to as CVE-2014-9463) will no longer be possible, and that the vBulletin team is not responsible in case something goes wrong.
The recommendation for administrators is to completely remove vBSEO from the system and choose a different tool for the purpose of SEO optimization.
