

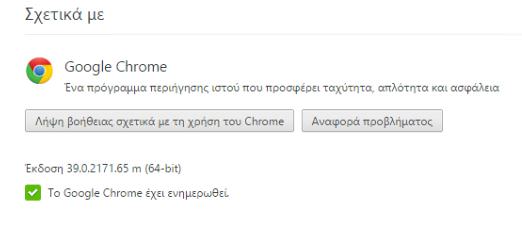
The Chrome development team has announced the release of Chrome 39 to the stable channel for Windows, Mac, and Linux. The new Chrome version 39.0.2171.65 comes with a long list of fixes and improvements, including:
64-bit support for Mac
A number of new applications and extension APIs
Many changes for more stability and better performance
Some of the changes are described in the change log.
You can download the new version from here, or directly from the Chrome you are using by going to the address
chrome://chrome/
Security fixes and Rewards
Note: Details of the bugs won't be announced until the majority of users have updated their programs to the new version. However, the company says that the update includes 42 security fixes. Below, they list the code fixes after suggestions made to them by external researchers and by Google's own security team. For more information, you can see the official Chromium.
[$500][389734] High CVE-2014-7899: Address bar spoofing. Credit to Eli Grey.
[$1500][406868] High CVE-2014-7900: Use-after-free in pdfium. Credit to Atte Kettunen from OUSPG.
[$1000][413375] High CVE-2014-7901: Integer overflow in pdfium. Credit to cloudfuzzer.
[$1000][414504] High CVE-2014-7902: Use-after-free in pdfium. Credit to cloudfuzzer.
[$3000][414525] High CVE-2014-7903: Buffer overflow in pdfium. Credit to cloudfuzzer.
[$2000][418161] High CVE-2014-7904: Buffer overflow in Skia. Credit to Atte Kettunen from OUSPG.
[$2000][421817] High CVE-2014-7905: Flaw allowing navigation to intents that do not have the BROWSABLE category. Credit to WangTao(neobyte) of Baidu X-Team.
[$500][423030] High CVE-2014-7906: Use-after-free in pepper plugins. Credit to Chen Zhang (demi6od) of the NSFOCUS Security Team.
[$7500][423703] High CVE-2014-0574: Double-free in Flash. Credit to biloulehibou.
[$5000][424453] High CVE-2014-7907: Use-after-free in blink. Credit to Chen Zhang (demi6od) of the NSFOCUS Security Team.
[$500][425980] High CVE-2014-7908: Integer overflow in media. Credit to Christoph Diehl.
[$500][391001] Medium CVE-2014-7909: Uninitialized memory read in Skia. Credit to miaubiz.
