

Do you notice that your computer is suddenly slowing down for some reason that you can't explain? It could be nothing, but it could be (Bot Net) that your computer is busy with other things. Among these is the attack by a hacker who has made the computer part or slave of a bot.

“How can this be? I use anti-virus software constantly to this day?”
The software used by Bots is clean and usually installed on the victim’s computer by the victim themselves, who has been tricked in some way. The software could appear as a legitimate product claiming to be an anti-virus scanner, when in fact it is malicious Scareware. Once installed, it opens a “door” on your system from where malware developers can install rootkits and applications that enable bot networks.
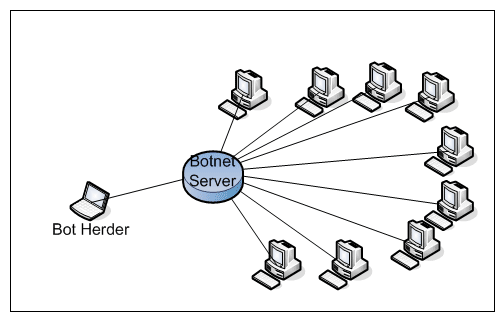
The botnet software effectively puts your computer at the hacker's disposal. It operates "normally" and waits to receive instructions from a master control terminal controlled by the botnet owner, who is usually a criminal.
The computer infection system, that is, those who are only involved in hacking systems, earn a lot of money by selling the rights to manage the infected computer to Bot Net.
You read that right, an infected computer can be "sold" without the permission of its owner.
A typical botnet can consist of tens of thousands of computers all controlled by a command and control terminal. Hackers use botnets because they allow them to combine the computing power and network of all infected computers to attack a single target. You know about distributed denial of service (DDoS) attacks.
These attacks are very powerful, and the target of the attack may not be able to manage the network and resources of a Bot Net that may contain 20,000 computers.
Some of the criminals, having such a “weapon” in their hands, also carry out blackmail to stop the attacks. Some businesses (although it is a bad policy) pay to have access to their systems again.
How do Bot Nets get so big?
The programmers who create bots can make a tidy profit tax-free. They often pay $250 or more for 1000 infected computers that can be slaved to a bot. Of course, the bad guys will use any means necessary to trick unsuspecting users into installing crapware. Through spam emails, or malicious links from forums and various other malicious websites, or anything else they can think of to get the victim to click on the malware installer.
How can we stop hackers from enslaving our computer?
1. Install a dedicated malware scanner
Your antivirus program may be awesome, but it's not so good at finding scareware, malware, rootkits, and other forms of malware. Consider something like Malwarebytes , which is known for finding malware that traditional antivirus programs often miss.
2. Watch out for fake anti-virus
In your search for an anti-malware program, you could end up installing something malicious if you don't cross-check the first opinion you read somewhere. Never install anything that was sent to you via email or from a pop-up window.
3. Back up your CLEAN system.
