

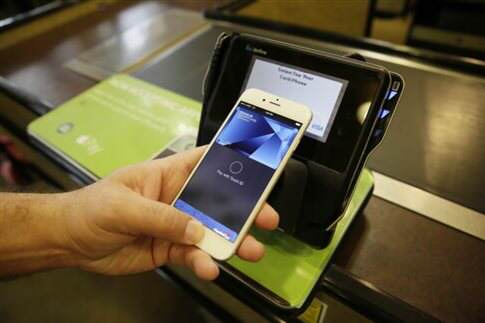
The Wall Street Journal reported on Thursday that there has been a "wave" of illegal transactions affecting the newly created iPhone payment system, Apple Pay
Stolen credit card details from major US store chains, specifically Target and Home Depot, are used for large purchases from Apple's own stores in the vast majority of cases (80%), the newspaper reported.
It remains unknown which Apple Pay allowed the stolen credit card details to be used.
However, it is known from the way Apple Pay works that the fingerprint reader on the iPhone does not certify that the prospective user of the credit card is also its owner, but simply the owner of the smartphone that contains its details.
It is also known that the cashier does not see the name, credit card number, or card security code.
We also know that Apple is not informed about payment history (what the user bought, where and how much).
Finally, when a user adds a credit or debit card to Apple Pay, their numbers are not stored on the device or on Apple's servers. Instead, a unique Device Account Number (DAN) is assigned, which is encrypted and securely stored in the iPhone's (or, in the future, Apple Watch's) Secure Element.
Authorization for each transaction is done with a unique code generated each time using the Device Account Number. Instead of the security code on the back of the credit card, Apple Pay dynamically generates a secure code.
However, a potential security gap is the way card issuers confirm that the card user is the authorized one, as has already been pointed out in the past.
Source: tech.in.gr
