

A virus targeting Android has been discovered by security researchers at Sophos Labs and spreads by sending SMS messages containing a download link to the first 99 contacts of victims.
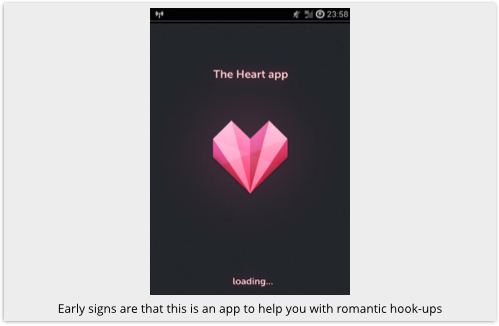
The malware is called XXshenqi in Chinese and “Heart App” in English.
After sending the SMS to the first 99 entries in the victim's contact list, the malware sends a confirmation message with the attacker's number.
The malware also asks victims to register and enter their personal information, including their ID card number and full name. Once the victim clicks the register button, the data entered by the victim will be sent to the attacker's number.
It also tricks victims into installing an add-on (com.android.Trogoogle) that does not appear on the regular “Apps” page. Trogoogle is able to read your incoming messages.
A 19-year-old software engineering student has been arrested by police in Shenzhen and accused of being the creator of the “Heart App” malware.
To remove the virus completely, go to Settings -> Applications -> Downloads and uninstall both "com.android.Trogoogle" and "XX 神器"
