

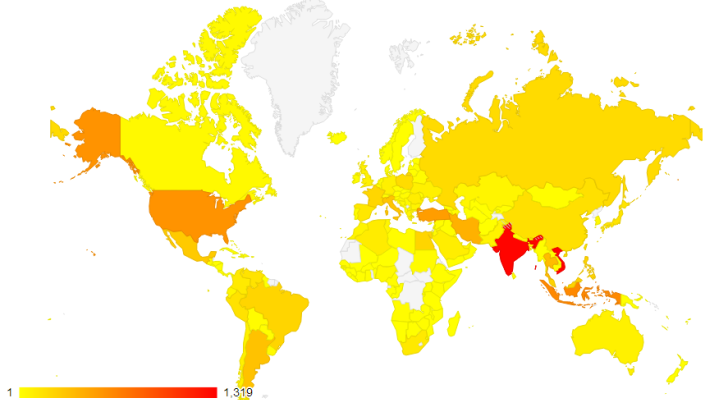
The Pushdo remains strong and evolving, as confirmed by the systems of the security company Bitdefender, which recorded approximately 200,000 unique IP addresses attempting to communicate with the domains of the Command and Control Servers.
Bitdefender purchased domains that had been created by Pushdo's DGA (Domain Generation Algorithm) algorithm for "sinkholing" purposes.
The company observed a steady increase in the number of IP addresses associated with infected computers attempting to connect to the botnet's command and control (C&C) servers to receive instructions.
In its latest report on the issue, Bitdefender states that the "research team saw Pushdo bots communicating with the central system from a staggering 183,909 unique IP addresses, from all over the world.".
The countries most affected by the malware continue to be India (21,768 infections) and Vietnam (20,043 infections), followed by Iran (9,787 infections) and the United States (9,001 infections).
Other affected countries are Turkey (8,865), Indonesia (8,240), Thailand (8,062), Argentina (6,212), Peru (5,828) and Mexico (5,447).
