

PAX Q80 payment terminals are at the center of three serious vulnerabilities that could allow an attacker on the same or a neighboring network to bypass checks, change settings, and even execute code with root privileges. ZDI listings were updated on August 14, 2026.
The disclosures concern CVE-2026-19908, CVE-2026-19909, and CVE-2026-19910. Their common feature is that they do not require certification, while ZDI describes the affected firmware as end-of-life and out of support. This significantly limits the options for enterprises using the model.
See also: Ghost Tap attack abuses NFC mobile payments
What the vulnerabilities in the PAX Q80 reveal
The first vulnerability, CVE-2026-19908, is in the XCB daemon. The lack of authentication checking allows an attacker with access to the neighboring network to gain access to functions that could reveal sensitive information and modify the terminal configuration. ZDI notes that the vulnerability can be combined with others to execute code as root.
CVE-2026-19909 concerns the parsing of AIP files by the installation process. By creating a symbolic link, an attacker can trick the installer into writing arbitrary files. The attack requires access from the neighboring network, but not an account, and can be used in conjunction with another vulnerability to execute code in the root environment.
See also: Active GeoServer SQL injection threatens exposed servers
The third vulnerability, CVE-2026-19910, is found in the application installer. The problem is insufficient verification of the cryptographic signature before installing an application. Thus, an attacker with access to the neighboring network could attempt to execute arbitrary code without authentication, with ZDI evaluating the possibility as a chain to root privileges.
The requirement for network proximity reduces the likelihood of a random attack by a remote user, but not the risk in a store or chain where the payment network is connected to other infrastructure. A compromised computer on the same network segment or an incorrect configuration can act as a starting point.
Why the situation is difficult for managers
The three ZDI alerts have different initial publication dates, but were updated together on August 14. The CVEs are listed with CVSS scores of 7.1, 7.5, and 7.5, respectively. Technical severity, however, is not the only issue: the timeline indicates that PAX had marked the referenced firmware as out of life.
According to ZDI-26-524, ZDI-26-525 , and ZDI-26-526, ZDI notified the company in April and noted disagreements regarding the impact on supported versions. The company later confirmed the issue in the reported firmware, while requesting an extension until April 2027.
ZDI does not list any available updates to fix the vulnerabilities. For CVE-2026-19908 and CVE-2026-19909, it states that users cannot upgrade to newer firmware, while for CVE-2026-19910, it notes that the software in question is no longer supported. The CVE Alert reports also document the absence of a specific fix.
The publication does not document exploitation in real-world attacks or provide a complete exploitation guide, so organizations should not assume that every PAX Q80 has already been compromised. However, an immediate assessment of its inventory and communication paths is needed, especially in environments where transactional data is being processed.
What businesses should do with PAX Q80
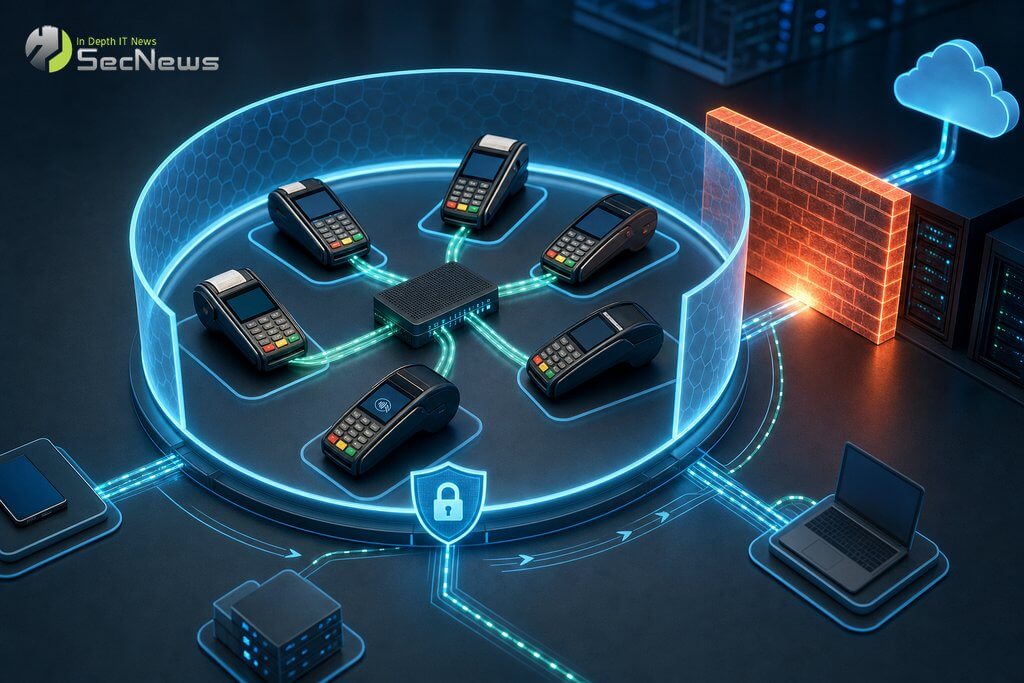
The only direct direction ZDI gives is to limit interaction with the product. In practice, those responsible should record each PAX Q80, check the firmware, and isolate the terminals on a separate network segment, without access from non-essential workstations or services.
At the same time, it is necessary to control connections to and from endpoints, restrict administrative access, and look for unusual configuration changes or application installation attempts. The absence of certification as a prerequisite does not mean that every device is exposed from the Internet, but it makes network segmentation a critical measure.
🔒 Protect your privacy with Proton VPN
Swiss VPN from the creators of Proton Mail — strict no-logs policy, strong encryption, and built-in NetShield that blocks ads, trackers, & malware.
- ✔ No-logs, based in Switzerland (except 14-Eyes)
- ✔ NetShield: blocks ads, trackers & malicious domains
- ✔ Covers all devices — free version available
The link is an affiliate link — SecNews may receive a commission at no additional cost to you. It does not affect the independence of our article writing.
Recording devices and their owners also helps ensure that old terminals are not left out of control. Every change in configuration must be documented, while access rules need to be reviewed after every change to the infrastructure.
See also: Three critical vulnerabilities in Emlog Assistant
The key takeaway for businesses is that an unsupported endpoint should not be treated as a regular device just waiting for the next update. Until there is a clear solution from the manufacturer, reducing network exposure and planning for a replacement is the most realistic line of defense.
